Ingeniero de sistemas y seguridad.Gamer en los ratos libres.Quiero compartir con todo sobre el mundo de la tecnología de manera mas fácil de entender y acercarla cada vez mas.
Nuevo Malware Umbrij Explotan OAuth para Acceso No Autorizado a Gmail, Vinculado al Grupo ToddyCat La Emergencia del Malware Umbrij El panorama de la ciberseguridad continúa evolucionando a medida que emergen nuevas amenazas, con un informe reciente que destaca las actividades de un actor de amenaza conocido como ToddyCat. Este grupo ha sido vinculado a…
New Umbrij Malware Exploits OAuth for Unauthorized Gmail Access, Linked to ToddyCat Group The Emergence of Umbrij Malware The cybersecurity landscape continues to evolve as new threats emerge, with a recent report highlighting the activities of a threat actor known as ToddyCat. This group has been linked to a sophisticated malware variant called Umbrij, which…
ChocoPoC RAT: Una Nueva Amenaza que Apunta a Investigadores de Vulnerabilidades a Través de Repositorios de Explotación Falsos Una Visión General de ChocoPoC RAT El panorama de la ciberseguridad enfrenta una nueva amenaza con la aparición de un software malicioso conocido como ChocoPoC RAT (Troyano de Acceso Remoto). Este sofisticado malware tiene como objetivo a…
ChocoPoC RAT: A New Threat Targeting Vulnerability Researchers Through Fake Exploit Repositories An Overview of ChocoPoC RAT The cybersecurity landscape is facing a new threat with the emergence of a malicious software known as ChocoPoC RAT (Remote Access Trojan). This sophisticated malware targets vulnerability researchers by embedding itself within fraudulent exploit code hosted on platforms…
Teen Extradited to the US in Connection with Scattered Spider Hacks: Implications for Cybersecurity Background and Context The recent extradition of a 19-year-old suspect in the notorious Scattered Spider hacking group has raised alarm bells in the cybersecurity community. The individual, who remains unnamed due to their age, has been implicated in a series of…
Aflac Data Breach: Insights into the Hack of Its Japan Subsidiary Background and Context The recent data breach at Aflac, a leading American insurance giant, has raised alarms across the cybersecurity landscape. The breach occurred after attackers infiltrated the systems of Aflac’s subsidiary in Japan, compromising sensitive personal and banking information of numerous individuals. This…
Highway Signs and Billboards at Risk: New Vulnerabilities in Daktronics Controllers Background and Context The digital landscape is an increasingly interconnected web of devices that includes everything from smartphones to public infrastructure systems like highway signs and billboards. These systems, which serve critical functions in urban and rural environments, are often overlooked in discussions about…
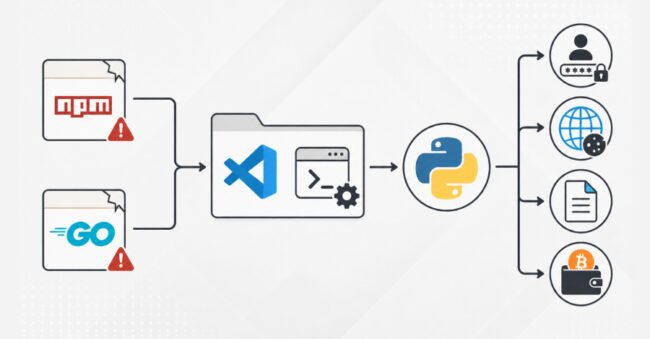
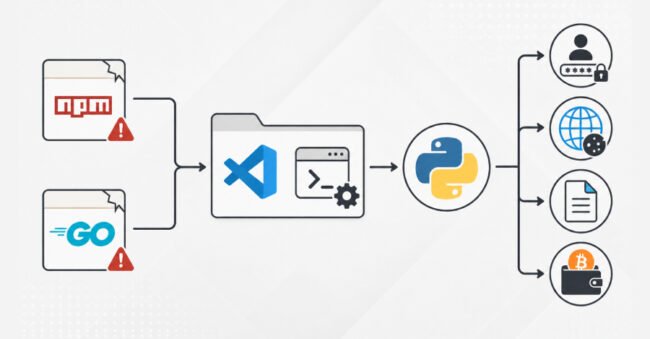
Alerta de Seguridad: Paquetes npm y Go Secuestrados Despliegan Infostealer de Python a través de Tareas de VS Code Descripción General del Ataque Investigaciones recientes en ciberseguridad han revelado hallazgos alarmantes respecto a dos paquetes npm comprometidos y varios paquetes de Go que han sido explotados para desplegar un malware de robo de información basado…
Security Alert: Hijacked npm and Go Packages Deploy Python Infostealer via VS Code Tasks Overview of the Attack Recent cybersecurity research has revealed alarming findings regarding two compromised npm packages and several Go packages that have been exploited to deploy a Python-based information-stealing malware. This malware targets multiple operating systems, including Windows, Linux, and macOS,…
Unmasking Deception: Ukraine’s Fight Against Russian Intelligence Cyber Operations Background and Context In recent years, the cyber battleground has become a significant front in geopolitical conflicts, especially in the context of Russia’s ongoing aggression against Ukraine. The Security Service of Ukraine (SSU), in collaboration with the U.S. Federal Bureau of Investigation (FBI), has revealed a…