Ingeniero de sistemas y seguridad.Gamer en los ratos libres.Quiero compartir con todo sobre el mundo de la tecnología de manera mas fácil de entender y acercarla cada vez mas.
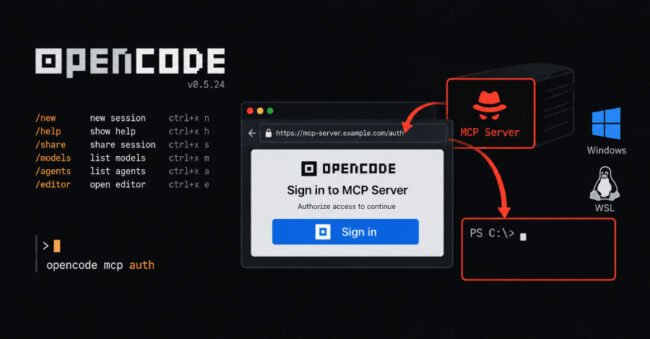
Critical OpenCode Vulnerability Exposes Windows and WSL Users to Remote Code Execution Risks Overview of the OpenCode Flaw A recently discovered vulnerability in OpenCode, an AI-powered coding assistant, has raised significant security concerns among developers using Windows and Windows Subsystem for Linux (WSL). This flaw enables malicious or compromised Model Context Protocol (MCP) servers to…
eMudhra’s Withdrawal from Certificate Business: A Wake-Up Call for Cybersecurity Background and Context The Indian tech landscape has witnessed significant growth, particularly in the realm of digital security and cryptography. eMudhra, one of the leading providers of digital certificates in India, announced its withdrawal from the certificate business following a serious security incident. This decision…
El Rol Crítico de Aprovechar la IA en la Prueba de Penetración Agentic Comprendiendo la Prueba de Penetración Agentic La prueba de penetración agentic (pentesting) es un enfoque innovador que aprovecha la inteligencia artificial (IA) para mejorar las medidas de ciberseguridad. Al utilizar modelos de propósito general, los equipos de seguridad de aplicaciones (AppSec) pueden…
The Critical Role of Harnessing AI in Agentic Penetration Testing Understanding Agentic Penetration Testing Agentic penetration testing (pentesting) is an innovative approach that leverages artificial intelligence (AI) to enhance cybersecurity measures. By utilizing general-purpose models, application security (AppSec) teams can initiate complex attack simulations against their web applications with minimal setup. This represents a significant…
Vasilek Backdoor: A Two-Year Cyber Intrusion in Russian Healthcare Networks Background and Context The recent revelation of a prolonged cyber intrusion targeting a Russian healthcare organization has underscored the escalating tensions in the realm of cybersecurity, particularly involving state-aligned hacktivist groups. The attack, attributed to a Belarusian group known as Partisan Zmiy, or Cyber Partisans,…
Incursión de APT28 en un Constructor Naval de la OTAN: Un Nuevo Panorama de Amenazas Introducción a APT28 APT28, también conocido por varios alias como BlueDelta, Fancy Bear y Forest Blizzard, es un grupo de ciberespionaje patrocinado por el estado, vinculado al gobierno ruso. El grupo ha estado activo durante más de una década y…
APT28’s Breach of NATO Naval Shipbuilder: A New Threat Landscape Introduction to APT28 APT28, also known by various aliases such as BlueDelta, Fancy Bear, and Forest Blizzard, is a notorious state-sponsored cyber espionage group linked to the Russian government. The group has been active for over a decade and is infamous for its sophisticated cyber…
ConnectWise Security Incident: Credential Resets as Cloud Backup Service Remains Offline Background and Context The recent cybersecurity incident at ConnectWise, a prominent player in the IT management and automation space, has raised alarm bells across the tech community. As organizations increasingly rely on cloud services for backup and data management, incidents like this not only…
Un Acelerador Web3 Malicioso Explota Paquetes npm para Distribuir Malware Dirigido a Entusiastas de la IA Descripción General del Falso Acelerador Web3 Un reciente informe de seguridad ha revelado un acelerador Web3 fraudulento que emplea paquetes npm maliciosos para propagar malware entre desarrolladores y usuarios que trabajan en las últimas tecnologías de inteligencia artificial. Al…
Malicious Web3 Accelerator Exploits npm Packages to Distribute Malware Targeting AI Enthusiasts Overview of the Fake Web3 Accelerator A recent security report has unveiled a fraudulent Web3 accelerator that is employing malicious npm packages to propagate malware among developers and users working on the latest artificial intelligence technologies. By masquerading as a legitimate platform offering…