Ingeniero de sistemas y seguridad.Gamer en los ratos libres.Quiero compartir con todo sobre el mundo de la tecnología de manera mas fácil de entender y acercarla cada vez mas.
Critical Docker Sandboxes Flaw Exposes macOS Hosts to Malicious Code Background and Context The recent discovery of a critical vulnerability in Docker Sandboxes, designated CVE-2026-77179, has sent shockwaves through the cybersecurity community. Docker, a widely adopted platform for developing, shipping, and running applications in containers, is trusted by developers and enterprises worldwide to provide a…
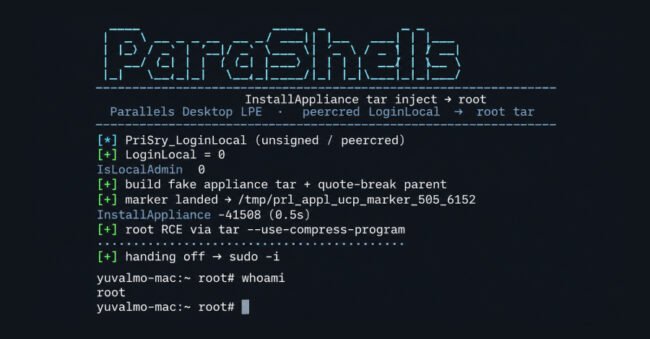
Fallo de Seguridad Crítico en Parallels Desktop para Mac: Usuarios No Administradores Pueden Elevar Privilegios Visión General del Fallo Una vulnerabilidad reciente descubierta en Parallels Desktop para Mac ha generado serias preocupaciones de seguridad, ya que permite que cuentas locales ordinarias ejecuten código con privilegios de root. Esto significa que los usuarios no administradores podrían…
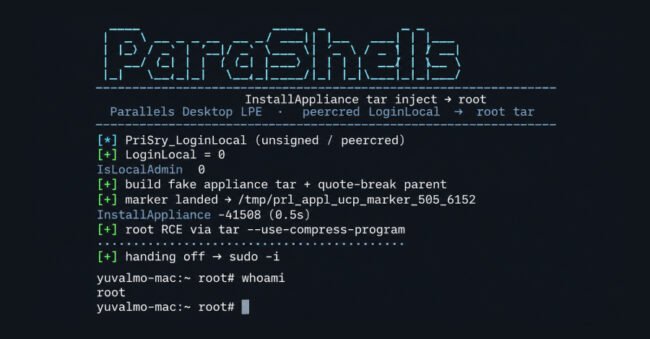
Critical Security Flaw in Parallels Desktop for Mac: Non-Admin Users Can Elevate Privileges Overview of the Flaw A recent vulnerability discovered in Parallels Desktop for Mac has raised serious security concerns, as it allows ordinary local accounts to execute code with root privileges. This means that non-admin users could potentially gain the highest level of…
Emerging Cyber Threats: Three Groups Target Russian Enterprises with Evolving Tactics Background and Context The cybersecurity landscape has become increasingly precarious, particularly for enterprises in Russia, which have recently faced a concerted effort from three distinct threat groups: NightEagle, Hacking Cat, and Toy Ghouls. According to reports from Kaspersky, these groups have implemented advanced techniques…
El malware BambooToken explota MQTT para ataques multiplataforma en Windows y Linux Descripción general del malware BambooToken Los investigadores en ciberseguridad han descubierto recientemente una nueva familia de malware, apodada BambooToken, que ha estado activa desde al menos febrero de 2023. Esta campaña de malware es notable por su uso del protocolo de Transporte de…
BambooToken Malware Exploits MQTT for Cross-Platform Attacks on Windows and Linux Overview of BambooToken Malware Cybersecurity researchers have recently unearthed a new family of malware, codenamed BambooToken, which has been active since at least February 2023. This malware campaign is notable for its use of the Message Queueing Telemetry Transport (MQTT) protocol, a lightweight messaging…
Microsoft’s AI Code of Conduct: Defining Boundaries for Cybersecurity in the Age of AI Background and Context The rapid advancement of artificial intelligence (AI) has transformed various sectors, including cybersecurity. As organizations increasingly rely on AI for defensive measures, the potential for misuse has sparked ethical and legal debates. The recent unveiling of Microsoft’s AI…
Red Heron Explota la Vulnerabilidad RCE de Gitea para Atacar a Organizaciones en Todo el Mundo Introducción al Incidente Una reciente violación de ciberseguridad descubierta por la Acronis Threat Research Unit (TRU) ha revelado las actividades de un actor de amenazas chino sospechoso conocido como Red Heron. Se informa que este grupo está aprovechando una…
Red Heron Exploits Gitea RCE Vulnerability to Target Organizations Worldwide Introduction to the Incident A recent cybersecurity breach uncovered by Acronis Threat Research Unit (TRU) has unveiled the activities of a suspected Chinese threat actor known as Red Heron. This group is reportedly taking advantage of a newly disclosed Remote Code Execution (RCE) vulnerability in…
DDRop Attack: A New Threat to Confidential Computing in Intel and AMD Systems Background and Context The landscape of cybersecurity is constantly evolving, with threats becoming increasingly sophisticated and varied. One of the most significant advancements in recent years has been the rise of **confidential computing**, a technology designed to protect sensitive data while it…