Ingeniero de sistemas y seguridad.Gamer en los ratos libres.Quiero compartir con todo sobre el mundo de la tecnología de manera mas fácil de entender y acercarla cada vez mas.
Critical Flaw in Canonical’s LXD and MicroCloud Exposes Clients to Impersonation Attacks Overview of the Vulnerability A severe security vulnerability has been identified in Canonical’s LXD and MicroCloud platforms, with a CVSS score of 10.0 marking it as critically dangerous. The flaw allows attackers to log in as trusted clients without needing the private keys…
NetamLoader Malware: A Sophisticated Threat to Asian Government Systems Background and Context In an alarming development that underscores the growing sophistication of cyber threats, Kaspersky has recently disclosed details about a malware strain dubbed **NetamLoader**, which specifically targets government organizations across Asia. This malware exploits a custom build of Windows 10 employed exclusively by government…
El FBI conecta a TraderTraitor de Corea del Norte con el histórico robo de criptomonedas de $6.43 mil millones en Binance Descripción general del robo La Oficina Federal de Investigaciones (FBI) ha vinculado el robo significativo de más de $6.43 mil millones en activos virtuales a TraderTraitor, un grupo de hackers de élite que opera…
FBI Connects North Korea’s TraderTraitor to Historic $6.43 Billion Crypto Heist on Binance Overview of the Heist The Federal Bureau of Investigation (FBI) has linked the significant theft of over $6.43 billion in virtual assets to TraderTraitor, an elite hacking group operating under the auspices of the North Korean regime. This attribution highlights the evolving…
Exploiting Vulnerabilities: The Threat of Unauthenticated Access in Ivanti Connect Secure Background and Context The recent announcement by the U.S. Cybersecurity and Infrastructure Security Agency (CISA) about the discovery of critical vulnerabilities in Ivanti Connect Secure (ICS) has sent shockwaves through the cybersecurity community. The vulnerabilities, identified as CVE-2026-111357 and CVE-2026-111358, are particularly alarming due…
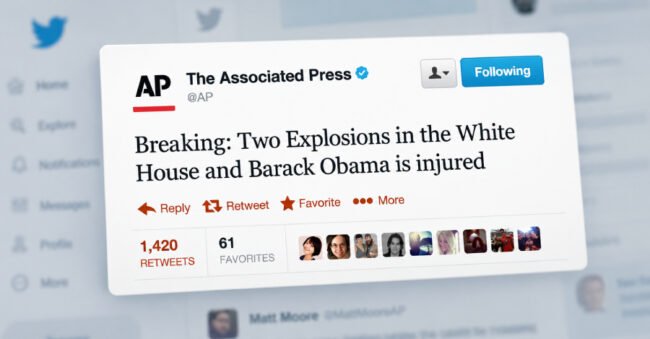
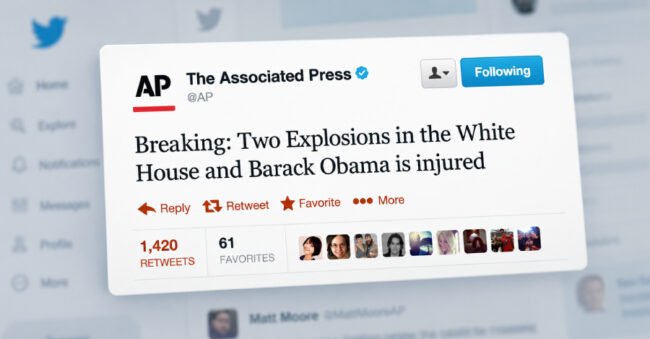
Hacker Sirio Sentenciado a 42 Meses por su Papel en un Tweet Falso que Causó una Crisis de Mercado de $136 Mil Millones Resumen del Caso Ahmad Umar Agha, un hacker sirio conocido por su alias en línea “Th3Pr0,” ha sido sentenciado a 42 meses de prisión por un tribunal federal de EE.UU. La condena…
Syrian Hacker Sentenced to 42 Months for Role in Fake Tweet That Caused $136 Billion Market Crisis Overview of the Case Ahmad Umar Agha, a Syrian hacker known by his online alias “Th3Pr0,” has been sentenced to 42 months in prison by a U.S. federal court. Agha’s conviction stems from a high-profile hacking conspiracy targeting…
Exploitation of Max-Severity GitLab Vulnerability Poses Significant Threat to Alpine Linux Background and Context The recent discovery of a critical vulnerability in GitLab, tracked as CVE-2026-97229, has sent shockwaves through the open-source community, particularly affecting users of Alpine Linux. This vulnerability allows unauthenticated attackers to execute arbitrary code on affected servers, effectively compromising their integrity…
Amenazas Cibernéticas Emergentes: Fallas Críticas en Cortafuegos, Trogans Bancarios en Renta, y Más Introducción: Una Doble Naturaleza de las Amenazas a la Ciberseguridad El panorama de la ciberseguridad está en constante evolución, y los informes recientes destacan una tendencia preocupante de ataques sofisticados y descuidos de seguridad. La última entrega de ThreatsDay describe vulnerabilidades críticas…
Emerging Cyber Threats: Critical Flaws in Firewalls, Banking Trojans for Rent, and More Introduction: A Dual Nature of Cybersecurity Threats The landscape of cybersecurity is constantly evolving, and recent reports highlight a disturbing trend of both sophisticated attacks and careless security lapses. The latest installment of ThreatsDay outlines critical vulnerabilities in firewall systems, the rental…