Ransomware Strikes Again: Osaka Metropolitan University Cancels Classes Amid Cyberattack

Ransomware Strikes Again: Osaka Metropolitan University Cancels Classes Amid Cyberattack

Ransomware Strikes Again: Osaka Metropolitan University Cancels Classes Amid Cyberattack Background and Context The recent cyber incident at Osaka Metropolitan University highlights the escalating threat posed by ransomware attacks to educational institutions worldwide. On Tuesday, the university announced a cancellation of classes due to a suspected ransomware attack that rendered crucial internal networks, emails, and…
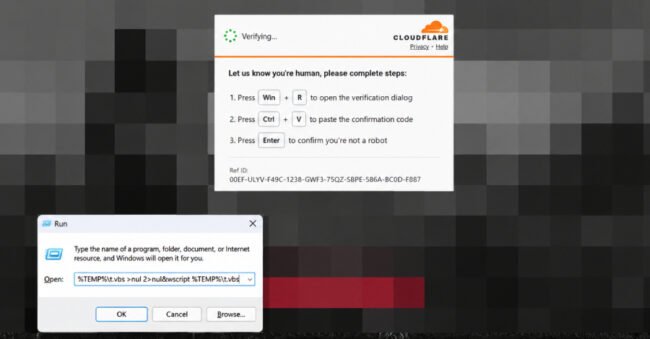
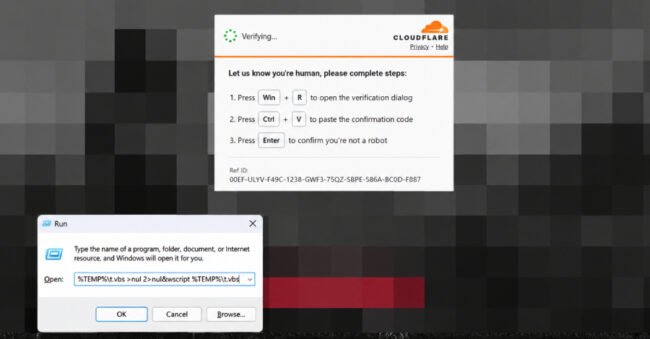
Nuevo Ataque ClickFix Aprovecha el Cache del Navegador para Evadir Limitaciones de Ejecución en Windows

Nuevo Ataque ClickFix Aprovecha el Cache del Navegador para Evadir Limitaciones de Ejecución en Windows Entendiendo los Ataques ClickFix En el paisaje en evolución de las amenazas de ciberseguridad, ClickFix representa una innovación notable en las metodologías de ataque. Como lo identificó el equipo de Inteligencia de Amenazas de Microsoft, este ataque aprovecha sitios web…

New ClickFix Attack Leverages Browser Cache to Evade Windows Run Limitations

New ClickFix Attack Leverages Browser Cache to Evade Windows Run Limitations Understanding ClickFix Attacks In the evolving landscape of cybersecurity threats, ClickFix represents a noteworthy innovation in attack methodologies. As identified by the Microsoft Threat Intelligence team, this attack leverages compromised websites to manipulate browser behavior, specifically targeting the cache. This sophisticated technique circumvents traditional…

Senate Takes Action: Bipartisan Bill to Bolster Healthcare Cybersecurity

Senate Takes Action: Bipartisan Bill to Bolster Healthcare Cybersecurity

Senate Takes Action: Bipartisan Bill to Bolster Healthcare Cybersecurity Background and Context In a significant move reflecting the rising concerns over cybersecurity in the healthcare sector, the U.S. Senate has passed a bipartisan bill aimed at strengthening protections against cyber threats. The urgency for such legislation is underscored by alarming statistics; last year alone, over…

Exposición de una Zero-Day de Alta Severidad en Citrix NetScaler, Dirigida a Despliegues de SAML

Exposición de una Zero-Day de Alta Severidad en Citrix NetScaler, Dirigida a Despliegues de SAML Descripción General de la Vulnerabilidad Citrix ha revelado recientemente una vulnerabilidad crítica de zero-day que afecta a su Controlador de Entrega de Aplicaciones NetScaler (ADC) y al Gateway de NetScaler. Identificada como CVE-2026-88779, esta falla ha recibido una puntuación CVSS…

High-Severity Zero-Day in Citrix NetScaler Exposed, Targeting SAML Deployments

High-Severity Zero-Day in Citrix NetScaler Exposed, Targeting SAML Deployments Overview of the Vulnerability Citrix has recently disclosed a critical zero-day vulnerability affecting its NetScaler Application Delivery Controller (ADC) and NetScaler Gateway. Identified as CVE-2026-88779, this flaw has been assigned a CVSS score of 8.7, categorizing it as high-severity and underscoring the potential risks associated with…

China-Aligned TA419 Targets U.S. AI Policy Experts with Credential Phishing Campaigns

China-Aligned TA419 Targets U.S. AI Policy Experts with Credential Phishing Campaigns

China-Aligned TA419 Targets U.S. AI Policy Experts with Credential Phishing Campaigns Background and Context The recent emergence of the cyber espionage group TA419, linked to China, highlights a troubling trend in the intersection of cybersecurity and artificial intelligence (AI) policy. Targeting experts from U.S. think tanks, universities, and legal organizations, TA419 has employed sophisticated credential…

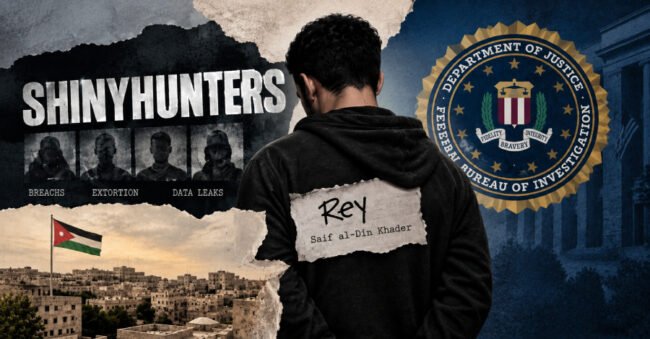
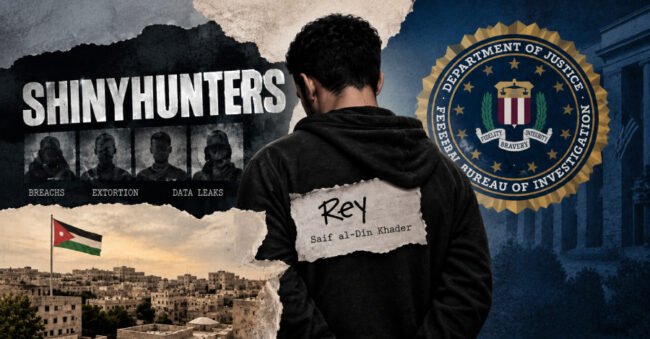
Desarrollo significativo en el cibercrimen: Sospechoso de ShinyHunters, Rey, detenido en Jordania

Desarrollo significativo en el cibercrimen: Sospechoso de ShinyHunters, Rey, detenido en Jordania Descripción general del grupo ShinyHunters El grupo ShinyHunters ha sido infame en el panorama de la ciberseguridad por su extensa participación en la extorsión digital y las filtraciones de datos. Operando desde 2020, han reclamado la responsabilidad de varios hacks de alto perfil,…

Significant Development in Cybercrime: ShinyHunters Suspect Rey Detained in Jordan

Significant Development in Cybercrime: ShinyHunters Suspect Rey Detained in Jordan Overview of the ShinyHunters Group The ShinyHunters group has been infamous in the cybersecurity landscape for its extensive involvement in digital extortion and data breaches. Operating since 2020, they have claimed responsibility for several high-profile hacks, harvesting sensitive information from companies and selling it on…

n0n Ransomware: An Emerging Threat in Cyber Extortion

n0n Ransomware: An Emerging Threat in Cyber Extortion

n0n Ransomware: An Emerging Threat in Cyber Extortion Background and Context The landscape of ransomware has been evolving at an alarming pace, with new groups perpetually entering the fray. The recent emergence of the n0n ransomware gang marks a significant development in this ongoing cybercrime saga. First detected in mid-September 2026, n0n quickly gained notoriety…