Ingeniero de sistemas y seguridad.Gamer en los ratos libres.Quiero compartir con todo sobre el mundo de la tecnología de manera mas fácil de entender y acercarla cada vez mas.
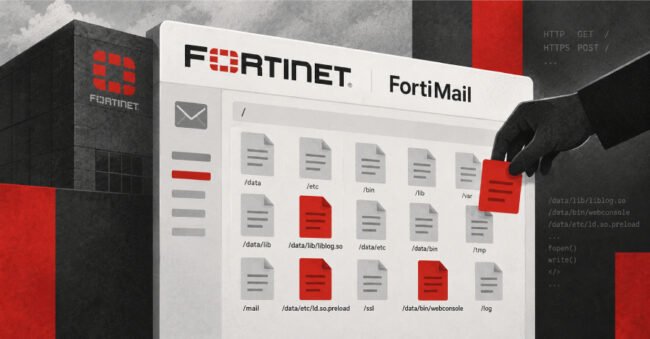
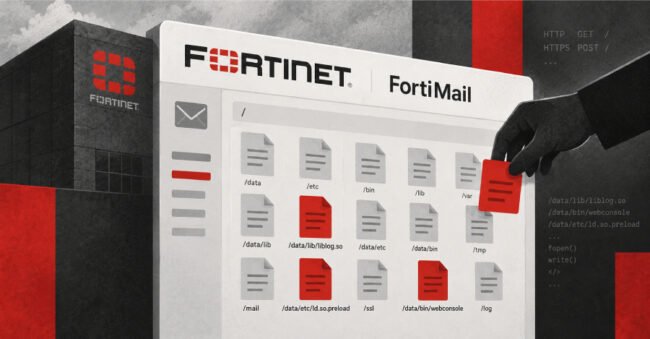
Critical Vulnerability in Fortinet FortiMail: The Urgent Threat of CVE-2026-104286 Background and Context The cybersecurity landscape is fraught with vulnerabilities that can jeopardize enterprise systems, yet few are as alarming as the recently discovered Fortinet FortiMail zero-day vulnerability, classified as CVE-2026-104286. This critical-severity path traversal vulnerability allows attackers to write arbitrary files to the system,…
La vulnerabilidad crítica de día cero de FortiMail expone los sistemas a ataques no autenticados Introducción a la vulnerabilidad La Agencia de Ciberseguridad y Seguridad de Infraestructura de EE. UU. (CISA) ha señalado recientemente una vulnerabilidad de seguridad significativa que afecta a Fortinet’s FortiMail, una solución de seguridad de correo electrónico de uso generalizado. Marcada…
Critical FortiMail Zero-Day Vulnerability Exposes Systems to Unauthenticated Attacks Introduction to the Vulnerability The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has recently flagged a significant security vulnerability affecting Fortinet’s FortiMail, a widely used email security solution. Marked as CVE-2026-104286, this flaw has received a critical CVSS score of 9.8, highlighting the potential severity of…
Modernizing Software Supply Chains: A Critical Imperative for Financial Services Background and Context As the digital landscape evolves, the financial services sector faces increasing scrutiny regarding its cybersecurity practices, particularly concerning software supply chains. The complex interplay between development teams and security leaders often leads to friction, as security protocols can be perceived as impediments…
Actualización Crítica de OpenSSL: Vulnerabilidad DTLS de Alta Severidad Plantea Riesgos de Fugas de Memoria Introducción a la Vulnerabilidad de OpenSSL El 29 de septiembre de 2026, OpenSSL anunció un defecto de alta severidad que afecta al protocolo de Seguridad de la Capa de Transporte de Datagramas (DTLS). Esta vulnerabilidad podría resultar en la exposición…
Critical OpenSSL Update: High-Severity DTLS Vulnerability Poses Memory Leak Risks Introduction to the OpenSSL Vulnerability On September 29, 2026, OpenSSL announced a high-severity flaw affecting the Datagram Transport Layer Security (DTLS) protocol. This vulnerability could result in unencrypted heap memory being exposed to the other end of a DTLS connection. The potential consequences of this…
CSuite Phishing Campaign Targets Microsoft 365 Users, Elevating Cyber Risks for U.S. Organizations Background and Context The cybersecurity landscape is witnessing an alarming surge in sophisticated phishing campaigns, particularly those targeting high-level executives within organizations. A recent campaign, traced by ANY.RUN researchers, has demonstrated a strategic focus on U.S.-based CSuite executives, with over half of…
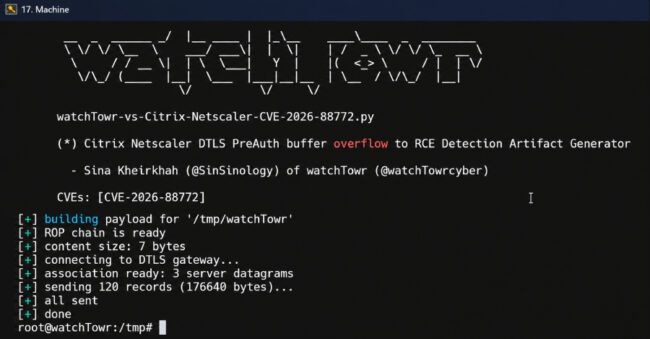
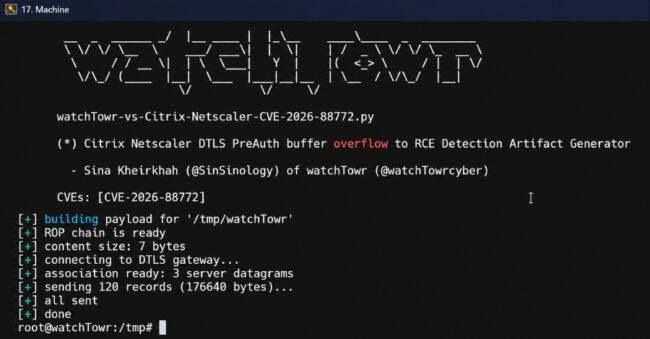
La vulnerabilidad crítica de Citrix NetScaler CVE-2026-88772 expone a los usuarios a riesgos de ejecución de shellcode Descripción general de CVE-2026-88772 Una vulnerabilidad de seguridad recientemente divulgada en Citrix NetScaler ADC y Gateway, rastreada como CVE-2026-88772, ha generado una alarma significativa entre los profesionales de ciberseguridad. Este fallo crítico, que recibió una alta puntuación en…
Critical Citrix NetScaler CVE-2026-88772 Vulnerability Exposes Users to Shellcode Execution Risks Overview of CVE-2026-88772 A recently disclosed security vulnerability in Citrix NetScaler ADC and Gateway, tracked as CVE-2026-88772, has raised significant alarm among cybersecurity professionals. This critical flaw, which received a high Common Vulnerability Scoring System (CVSS) score of 9.5, is categorized as a memory…
French Tax Data Theft Exposes Vulnerabilities in Cybersecurity Framework Background and Context The recent incident involving the theft of tax data from France’s tax administration has underscored significant vulnerabilities within governmental cybersecurity frameworks. In June and July 2023, attackers exploited stolen passwords belonging to tax administration staff, leading to the unauthorized access and extraction of…