Security Breach: Stolen Fireworks AI Key Compromises Claude Code Extension on Cursor
Overview of the Incident
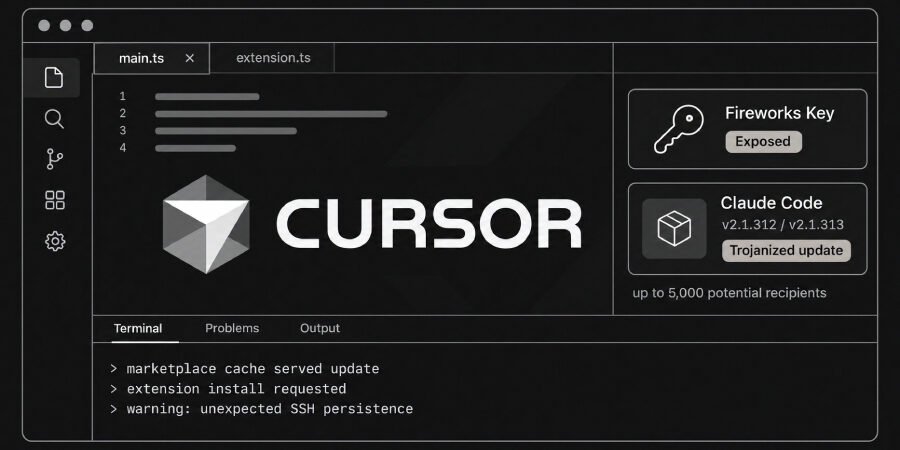
The recent breach involving the Claude Code extension, hosted on Cursor’s extension marketplace, has raised significant concerns within the tech community. According to a statement from Cursor, the incident originated from the theft of an access key that was originally issued to Fireworks AI. This breach highlights vulnerabilities associated with third-party integrations and the management of API keys.
The Role of Fireworks AI
Fireworks AI, a platform that enhances productivity through advanced machine learning capabilities, inadvertently became the focal point of a significant security incident. The exposed access key, which was intended for Fireworks’ internal use, was mishandled and came into the hands of a malicious actor.
- Access keys are critical for securing API communications.
- Improper management of sensitive credentials can lead to unauthorized data access.
Impact on Cursor and Anthropic
Cursor’s marketplace allowed for the distribution of various code extensions, including the popular Claude Code extension developed by Anthropic. The unauthorized access to Claude Code extension has serious implications not just for Cursor but also for Anthropic.
- The integrity of the Claude Code extension is now in question.
- Users may have been exposed to modified or trojanized code.
- Cursor’s reputation as a safe marketplace could be damaged, leading to loss of user trust.
Expert Analysis on API Security
The incident serves as a critical reminder of the importance of API security management. Experts stress the need for robust security protocols to prevent similar breaches in the future.
- Proper Key Rotation: Regularly changing access keys can mitigate the risk of long-term exposure.
- Granular Access Controls: Limiting permissions can minimize the damage potential if a key is compromised.
- Monitoring and Logging: Keeping track of API key usage can help identify unauthorized access early.
Implications for Future Security Practices
The breach not only jeopardizes the involved companies but also sends a strong message to the tech industry at large. As integrations become more complex, the importance of safeguarding sensitive credentials cannot be overstated. Organizations must work to enhance their security frameworks to protect against such threats.
- Investing in employee training regarding security best practices.
- Leveraging tools for automatic key management and rotation.
- Implementing multi-factor authentication for critical services.
Conclusion
The revelation of a compromised Claude Code extension highlights serious vulnerabilities arising from poor key management practices at third-party vendors like Fireworks AI. As the digital landscape evolves, so too must the cybersecurity measures employed by organizations to safeguard their assets.
Source: thehackernews.com