Exploiting the Cloud: Antino Backdoor Targets Asian Government Organizations in Espionage Campaign
Introduction to the Antino Backdoor
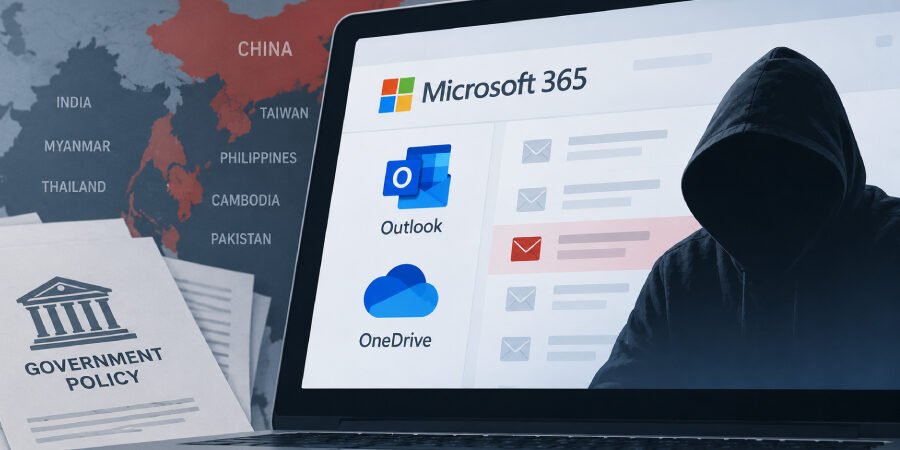
A newly discovered cyber espionage campaign has raised alarms across Asia as a China-nexus threat actor targets government and policy organizations. The campaign utilizes a sophisticated backdoor, codenamed Antino, allowing for extensive data exfiltration and control. Cisco Talos, a leading threat intelligence group, is actively monitoring this incident, providing crucial insights into the technological nuances and implications for cybersecurity globally.
Targeted Organizations and Geographic Scope
The Antino backdoor primarily focuses on several key countries in Asia, including:
- Taiwan
- India
- The Philippines
- Cambodia
- Pakistan
- Thailand
- Myanmar
This extensive targeting underscores the strategic interests that may underlie the espionage efforts, possibly aiming to gather intelligence on political, military, and economic contexts in the region.
Operational Mechanics of the Antino Backdoor
The Antino backdoor employs unique communication mechanisms that leverage widely used platforms such as Microsoft’s Outlook and OneDrive. This approach allows threat actors to establish command and control (C2) channels effectively, blending malicious activity with everyday organizational workflows. Some operational characteristics include:
- Use of email as an initial infiltrative vector, enabling seamless integration into existing communication systems.
- Deployment of scripts and payloads that can be activated by simply accessing shared OneDrive files.
- Geolocation tactics to avoid detection, facilitating targeted surveillance on particular individuals or organizations.
Such methods highlight the adaptability of modern attacks, capitalizing on trusted services to bypass traditional security measures.
Context of the Cybersecurity Landscape
The emergence of the Antino backdoor comes at a time of escalating cyber tension in Asia, where state-sponsored cyber espionage has increasingly become a tool for geopolitical leverage. Experts in cybersecurity suggest that the timing is critical, as nations are often engaged in sensitive negotiations and strategic military alignments in the region. The implications of this can be profound:
- Increased scrutiny of governmental cybersecurity protocols may lead to higher investments in defensive measures.
- Countries may seek to develop stronger international cooperative frameworks to combat state-sponsored cyber threats.
- Enhanced legislation regarding digital sovereignty and data protection may emerge as a response to such breaches.
Expert Analysis and Implications
Cybersecurity professionals express concern over the technical sophistication demonstrated by the Antino backdoor. According to Dr. Lisa Tran, a cybersecurity analyst at a major tech firm, “The operational strategies employed by the Antino backdoor signal a growing trend where cybercriminals leverage trusted platforms to facilitate espionage, thereby complicating the existing security protocols that organizations must enforce.” This shifting paradigm necessitates new methodologies in threat detection and incident response.
Moreover, the geopolitical implications of publicly attributed cyber campaigns could intensify diplomatic conflicts among impacted countries, especially if any sensitive data gathered is publicly disclosed or used to manipulate regional politics.
Conclusion
The discovery and ongoing investigation of the Antino backdoor by Cisco Talos serves as a vital reminder of the persistent threats posed by cyber espionage in today’s interconnected world. As government and policy organizations across Asia work to fend off these attacks, focus must be placed not only on immediate defensive tactics but also on long-term strategy evaluations to mitigate future risks.
Source: thehackernews.com