Assessing CVE Exploitability: A New Challenge in Cybersecurity
The Rise of Common Vulnerabilities and Exposures (CVEs)
Common Vulnerabilities and Exposures (CVEs) are fundamental to understanding cybersecurity risks in various software and systems. As new CVEs are reported, evaluating their potential threat level becomes crucial. A new CVE might have a high severity score, but that alone does not confirm that it can be exploited within a specific environment. This opens the door to essential questions regarding the ongoing vulnerability management process.
The Implications of Rapid Exploit Development
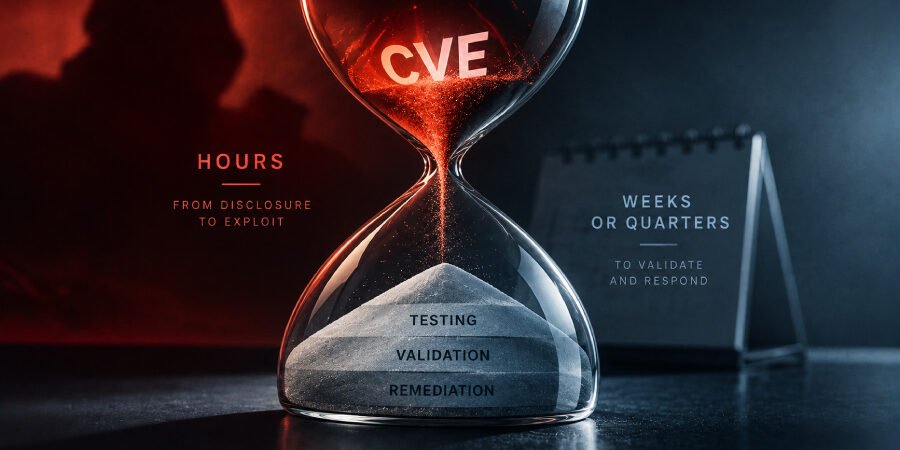
Mythos-class AI technologies are shortening the timeframe between disclosure and real-world exploitation of vulnerabilities. As AI continues to evolve, it enables attackers to leverage newly disclosed vulnerabilities faster than ever before. This shift necessitates a reevaluation of traditional security practices that often rely on outdated risk assessment cycles, typically conducted weekly or quarterly.
The Importance of Contextual Analysis
Understanding whether a CVE is exploitable requires a deep contextual analysis that incorporates several factors:
- Environment Specificity: Different environments may be configured in ways that mitigate the risk associated with a CVE.
- Version Discrepancies: The specific version of the software in use plays a critical role in determining whether a CVE can be exploited.
- Existing Security Controls: Robust security measures may thwart exploitation attempts even if a CVE has been identified.
Mitigating the Risk of Unexploited CVEs
To combat the threats posed by rapidly developing exploits, organizations need to adopt more proactive vulnerability management strategies. Here are several recommendations:
- Immediate Risk Assessment: Perform rapid assessments whenever a new CVE is disclosed.
- Continuous Monitoring: Implement automated monitoring systems to track potential exploits in real-time.
- Cross-Department Communication: Ensure that security teams work closely with IT and development teams to understand the full context of vulnerabilities.
Preparing for the Future of Exploitability Analysis
Organizations must reimagine their approach to vulnerability management to keep pace with evolving threats. Investment in training, tools, and resources for deeper analysis will become increasingly essential as the threat landscape transforms with advancements in AI and other technologies.
Conclusion
The gap between vulnerability disclosure and exploit readiness is narrowing, necessitating an agile response from security teams. Understanding the exploitability of new CVEs isn’t just a matter of assessing severity scores—it’s about context, risk management, and proactive security measures that adapt to the changing threat environment.
Source: thehackernews.com