Atlassian Data Center Vulnerability Sparks Immediate Exploitation Risks in Major Products
Overview of the Vulnerability
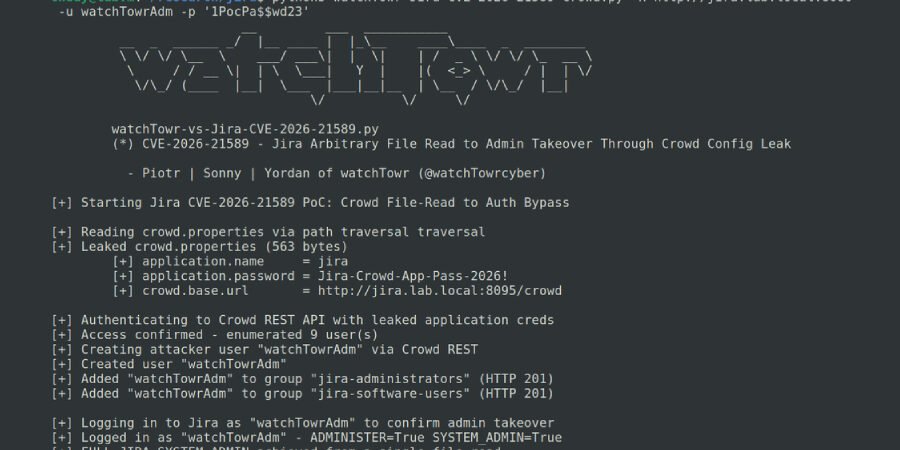
A recently disclosed security flaw in Atlassian Data Center products has raised significant alarm among IT professionals and cybersecurity experts. This critical vulnerability, identified as CVE-2026-21589, carries a high Common Vulnerability Scoring System (CVSS) score of 9.3. The flaw potentially enables unauthorized access to sensitive files, posing a significant risk to organizations using these platforms.
Impacted Products
The arbitrary file access flaw is present in several widely used Atlassian products, including:
- Bitbucket Data Center
- Confluence Data Center
- Jira Service Management Data Center
- Jira Software
These applications are integral to many enterprises, facilitating collaboration and project management. Therefore, the implications of this vulnerability could be catastrophic if left unaddressed.
Exploitation Timeline
Shortly after the vulnerability’s details were made public, threat actors began attempting to exploit the flaw within a mere two hours. This rapid response highlights the urgency with which malicious entities monitor security disclosures and seek to capitalize on them. The speed of these attempts underscores a significant trend in cybersecurity, where attackers are increasingly exploiting zero-day vulnerabilities swiftly after they are revealed.
Security Implications
The existence of such a critical vulnerability poses several security implications for organizations relying on Atlassian products:
- Data Breach Risks: Unauthorized access could lead to data breaches, exposing sensitive organizational and customer information.
- Regulatory Consequences: Companies may face legal repercussions for failing to protect sensitive data, especially in regulated industries.
- Reputation Damage: Public knowledge of an exploit could damage an organization’s reputation, diminishing trust among customers and partners.
Organizations are urged to conduct immediate risk assessments to understand their exposure to this vulnerability.
Mitigation Strategies
To safeguard against potential exploitation, experts recommend several mitigation strategies:
- Update Software: Immediately apply patches provided by Atlassian to all affected products.
- Monitor Systems: Implement monitoring tools to detect any unauthorized access attempts or unusual activity on systems running the impacted applications.
- Conduct Audits: Regularly audit security policies and access control mechanisms to enhance organizational security posture.
These proactive measures are essential in minimizing the potential impact of such vulnerabilities.
Conclusion
The recently disclosed CVE-2026-21589 flaw in Atlassian Data Center products illustrates the continuing challenges faced by organizations in securing their digital environments. With exploitation attempts surfacing almost immediately following the public disclosure, the need for robust security practices and vigilance has never been more critical. Organizations must prioritize prompt patching and engage in ongoing security assessment to protect against evolving threats.
Source: thehackernews.com