Critical FortiMail Zero-Day Vulnerability Exposes Systems to Unauthenticated Attacks
Introduction to the Vulnerability
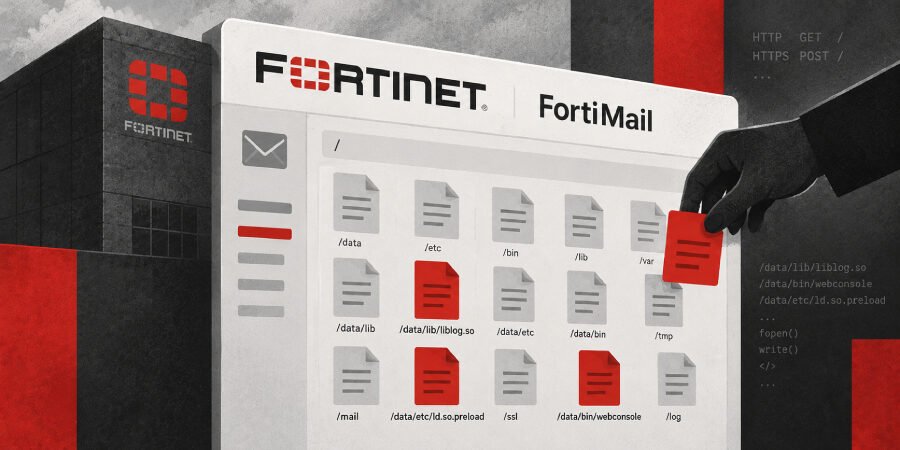
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has recently flagged a significant security vulnerability affecting Fortinet’s FortiMail, a widely used email security solution. Marked as CVE-2026-104286, this flaw has received a critical CVSS score of 9.8, highlighting the potential severity of its impact. The issue allows unauthenticated attackers to perform arbitrary file writes on the affected systems, which poses a substantial risk to organizations relying on FortiMail for secure email communications.
Details of the CVE-2026-104286 Exploit
According to reports, the vulnerability stems from improper input validation within the FortiMail application. This oversight enables attackers to bypass authentication mechanisms, thereby granting them unauthorized access to the underlying system. The implications of this vulnerability are profound, as it allows for a wide range of malicious activities, including:
- Uploading malicious files to the server
- Modifying or deleting existing files, potentially compromising sensitive data
- Launching further attacks from the compromised system, such as lateral movement within the network
Scope of the Threat
FortiMail is utilized by numerous organizations globally, making this flaw particularly egregious. Given its crucial role in securing email communications, the exploitation of this vulnerability could have severe consequences, including:
- Data breaches that expose sensitive information
- Disruption of email services for affected organizations
- Potential loss of customer trust and reputational damage
Active exploitation of this vulnerability has already been reported, emphasizing the urgent need for organizations to assess their exposure to this threat and implement necessary mitigations.
CISA’s Response and Recommended Actions
In light of the active exploitation, CISA has included CVE-2026-104286 in its Known Exploited Vulnerabilities (KEV) catalog. This inclusion serves as a critical alert to organizations to prioritize the patching of vulnerable systems. CISA recommends that organizations take the following actions:
- Immediately apply any available security patches from Fortinet.
- Review and enhance security configurations related to FortiMail.
- Monitor network traffic for unusual activity that may indicate exploitation attempts.
Expert Analysis on Vulnerability Management
Experts in cybersecurity stress the importance of a proactive approach to vulnerability management. This situation highlights several key best practices organizations should adopt:
- Regularly update and patch software to defend against known vulnerabilities.
- Implement a robust monitoring system that can detect unauthorized access or anomalies in system behavior.
- Conduct employee training to recognize phishing attempts and other social engineering tactics that may accompany such vulnerabilities.
The FortiMail incident serves as a stark reminder of the evolving threat landscape and the necessity for organizations to remain vigilant in their cybersecurity efforts.
Conclusion
The discovery of CVE-2026-104286 underscores a critical security challenge facing many organizations that utilize FortiMail for their email security needs. As attacks exploiting this vulnerability are already in progress, it is imperative for all impacted entities to act swiftly to mitigate the risks. Continuous vigilance, timely patching, and proactive security measures are essential to safeguard against such vulnerabilities in the dynamic cyber threat landscape.
Source: thehackernews.com