Malicious Web3 Accelerator Exploits npm Packages to Distribute Malware Targeting AI Enthusiasts
Overview of the Fake Web3 Accelerator
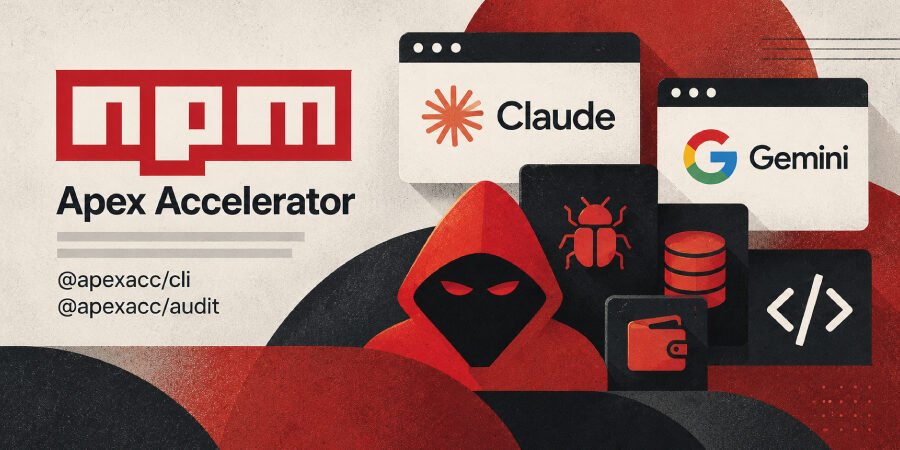
A recent security report has unveiled a fraudulent Web3 accelerator that is employing malicious npm packages to propagate malware among developers and users working on the latest artificial intelligence technologies. By masquerading as a legitimate platform offering perks such as free AI credits for Anthropic Claude and Google Gemini, the fake accelerator has successfully enticed individuals into downloading compromised software.
How the Malware is Distributed
The fake accelerator utilizes the npm (Node Package Manager) ecosystem to distribute its harmful payloads. Npm is widely used in the JavaScript community for package management, making it a lucrative target for cybercriminals. Here’s a breakdown of the methods employed:
- Malicious Packages: The impersonation of legitimate npm packages to deliver malware disguised as coding tools and security audits.
- Information Stealers: Tools that harvest sensitive user data from compromised systems, affecting both Windows and macOS users.
- Backdoors: Code that opens unauthorized access to the attackers, allowing them to control infected machines remotely.
Targeting Developers and AI Enthusiasts
The timing of this attack is particularly noteworthy, as interest in Web3 technologies and AI applications is at an all-time high. Developers seeking to leverage cutting-edge AI capabilities can easily fall victim to these scams, especially when promising resources are offered at no cost. The lure of free AI credits has proven to be an effective strategy for attracting potential victims.
Implications for the Tech Community
This incident raises several important concerns within the tech community:
- Trust and Safety: The incident highlights the need for heightened security measures within package management systems, reflecting ongoing challenges in ensuring the integrity of third-party dependencies.
- Increased Risk for AI Development: As AI tools become more intertwined with coding practices, vulnerabilities in associated technologies pose risks not only to developers but also to the wider ecosystem.
- Outdated Security Practices: The attack underscores the necessity for developers to adopt more rigorous auditing and security practices when integrating third-party packages.
Expert Analysis
Experts stress the importance of vigilance when downloading and using npm packages, especially from lesser-known sources. “Cybercriminals are becoming increasingly adept at exploiting trusted platforms, and the burgeoning interest in AI creates an additional vector for these types of attacks,” said a cybersecurity analyst from Elastic. “Education and awareness are key to mitigating these threats.”
Conclusion
The recent revelations about the fake Web3 accelerator using npm packages to disseminate malware serve as a stark reminder of the ongoing challenges in the cybersecurity landscape. As developers push forward in the realms of AI and Web3, maintaining security best practices will be essential in safeguarding sensitive data and ensuring the integrity of development environments.
Source: thehackernews.com