Critical Oracle E-Business Suite Vulnerability Under Attack Following Recent Patch Release
Overview of CVE-2026-101767
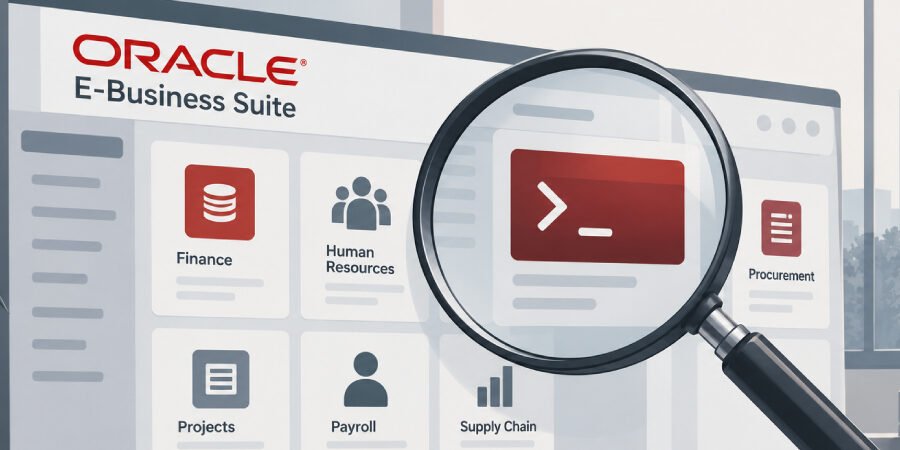
A newly identified vulnerability in Oracle E-Business Suite (EBS), designated as CVE-2026-101767, has drawn significant attention from cybercriminals just days after a critical security patch was released. Classified with a CVSS score of 9.8, this flaw pertains to improper authentication within the Oracle Application Object Library, leaving systems susceptible to remote code execution (RCE) attacks. Security firm Defused Cyber has reported increasing activity from threat actors probing for exploitation of this vulnerability.
The Nature of the Vulnerability
The improper authentication flaw allows attackers to bypass security measures, potentially gaining unauthorized access to sensitive system components. Given the central role of Oracle E-Business Suite in managing enterprise operations, the implications of such a security breach could be severe, including data exfiltration, system manipulation, or even complete takeover of impacted systems.
- CVSS Score: 9.8 (Critical)
- Vulnerability Type: Improper Authentication
- Impacted Component: Oracle Application Object Library
- Threat Level: High, due to its potential for remote exploitation
Recent Exploitation Attempts
Within days of the vulnerability’s disclosure and subsequent patching, various threat actor groups initiated probing activities aimed at identifying unpatched systems. Findings by Defused Cyber indicate a noticeable increase in automated scanning tools being used to locate vulnerable installations of Oracle EBS on the internet. This highlights the urgency for organizations to promptly implement security updates.
Implications for Businesses
Organizations using Oracle E-Business Suite face critical risks if they do not adopt a proactive stance on cybersecurity. The aftereffects of a successful exploitation could be far-reaching and costly, including:
- Loss of sensitive financial and operational data
- Financial losses due to downtime and recovery efforts
- Damage to reputation and customer trust
- Potential legal ramifications due to data breaches
Recommended Actions for Organizations
In light of this imminent threat, cybersecurity experts advise immediate action for organizations utilizing Oracle EBS:
- Apply the Latest Security Patches: Ensure the latest Oracle security updates are applied without delay.
- Conduct Regular Vulnerability Assessments: Frequently scan systems for vulnerabilities and ensure compliance with security best practices.
- Monitor for Unusual Activities: Implement robust monitoring for suspicious behaviors that may indicate exploitation attempts.
- Enhance Security Awareness Training: Educate employees on phishing risks and safe internet practices.
Conclusion
The recent discovery of the CVE-2026-101767 vulnerability in Oracle E-Business Suite underscores the ongoing battle between cybersecurity defenses and evolving attack strategies. As hackers actively seek to exploit newly discovered flaws, organizations must be vigilant and proactive in addressing potential cybersecurity threats to safeguard their operations and data integrity.
Source: thehackernews.com