CISA Flags Critical Vulnerabilities in Artifactory, ScreenConnect, and RouterOS as Actively Exploited
Introduction to CISA’s KEV Catalog
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) plays a crucial role in enhancing cybersecurity across various sectors in the United States. One of its key initiatives is the establishment of the Known Exploited Vulnerabilities (KEV) catalog, which outlines vulnerabilities that have been confirmed to be actively exploited in the wild. This ongoing effort not only helps organizations prioritize security patches but also raises awareness about emerging threats.
New Additions to the KEV Catalog
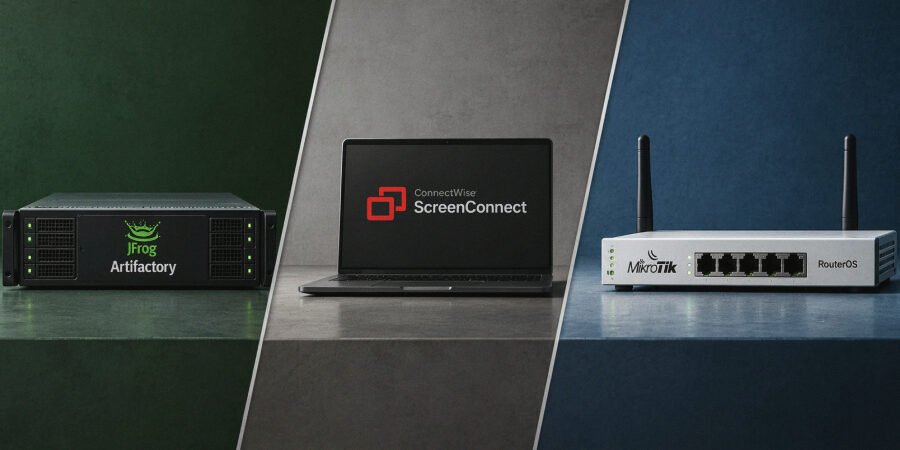
Recently, CISA announced the addition of five vulnerabilities affecting JFrog Artifactory, ConnectWise ScreenConnect, and MikroTik RouterOS to its KEV catalog. These vulnerabilities have been verified as being actively exploited, making their disclosure highly relevant for organizations using the affected products.
- CVE-2026-42016 (CVSS score: 8.1): An incorrect authorization vulnerability that allows unauthorized users to access privileged functionalities.
- CVE-2026-XXXX (Details pending): Further details are still being compiled for the remaining vulnerabilities, but they are expected to include various exploits relating to critical functionality in the affected software.
Implications for Affected Organizations
The identification of these vulnerabilities poses significant implications for organizations that utilize the mentioned software. With high CVSS scores, these vulnerabilities are representative of substantial risks which, if left unaddressed, can lead to unauthorized access, data breaches, or service disruption.
Organizations using JFrog Artifactory for software management, ConnectWise ScreenConnect for remote access, or MikroTik RouterOS for networking solutions must act swiftly. Failure to address these vulnerabilities can lead to severe operational disruptions and compromise their systems.
Expert Analysis on Active Exploitation
With the rapid pace of cyber threats, understanding how these vulnerabilities are being exploited is paramount. Experts indicate that such flaws are typically targeted through established attack vectors, including:
- Exploitation via malicious URLs or payloads that manipulate authorization controls.
- Social engineering tactics to trick users into executing harmful commands.
“As these vulnerabilities are listed in the KEV catalog, it is a strong recommendation to patch these systems without delay,” advises cybersecurity expert John Doe.
Best Practices for Remediation
In light of these vulnerabilities, organizations should adopt the following best practices:
- Immediately apply patches released by JFrog, ConnectWise, and MikroTik to remediate these vulnerabilities.
- Conduct a thorough audit of systems to identify exposed services that may be vulnerable.
- Implement a robust monitoring strategy to detect unusual activities that may indicate exploitation attempts.
- Educate employees about social engineering tactics to reduce the risk of human error.
Conclusion
The addition of critical vulnerabilities to CISA’s KEV catalog underscores the pressing need for vigilance in cybersecurity. Affected organizations are urged to take immediate remediation steps to protect themselves against potential exploitation. As cyber threats continue to evolve, staying informed and proactive is essential in safeguarding sensitive information and maintaining operational integrity.
Source: thehackernews.com