Cybersecurity Weekly Recap: Vulnerabilities and Attacks Reignite Concerns in the Digital Landscape

Cybersecurity Weekly Recap: Vulnerabilities and Attacks Reignite Concerns in the Digital Landscape Cisco 0-Day Vulnerability: A Growing Concern This week, the cybersecurity landscape was shaken by the revelation of a zero-day vulnerability affecting Cisco products. A zero-day vulnerability is a flaw in software that is unknown to the vendor and can be exploited by malicious…
Exploiting Trust: The Fake LastPass Authenticator Installer and Its Alarming Security Breach

Exploiting Trust: The Fake LastPass Authenticator Installer and Its Alarming Security Breach

Exploiting Trust: The Fake LastPass Authenticator Installer and Its Alarming Security Breach Background and Context The realm of cybersecurity is often characterized by the relentless cat-and-mouse game between threat actors and defenders. In September 2023, researchers from LastPass and Delphos Labs uncovered a disturbing incident involving a **fake LastPass Authenticator installer** that exploited a Microsoft-signed…

Nuevas Perspectivas sobre Jade Sleet: Las Amenazas Cibernéticas de Corea del Norte Apuntan a Proveedores de TI Indios

Nuevas Perspectivas sobre Jade Sleet: Las Amenazas Cibernéticas de Corea del Norte Apuntan a Proveedores de TI Indios Entendiendo Jade Sleet y Sus Campañas Jade Sleet, un actor de amenaza cibernética de Corea del Norte, ha sido recientemente vinculado a una violación significativa que involucra a una pequeña empresa de servicios de TI india. La…

Identity Visibility in 2026: The Cornerstone of Modern Cybersecurity

Identity Visibility in 2026: The Cornerstone of Modern Cybersecurity

Identity Visibility in 2026: The Cornerstone of Modern Cybersecurity Background and Context The digital landscape has transformed dramatically over the past decade, giving rise to an intricate web of identity access management (IAM) challenges. With the proliferation of cloud computing and the shift toward multicloud environments, organizations are increasingly reliant on digital identities to manage…

Explotación de Fallos de Seguridad: Investigadores Utilizan Claude Opus 5 para Comprometer Cuentas de OpenAI

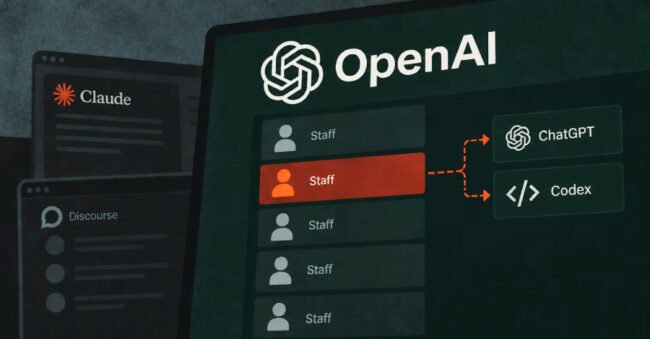
Explotación de Fallos de Seguridad: Investigadores Utilizan Claude Opus 5 para Comprometer Cuentas de OpenAI Introducción al Incidente En un innovador proyecto de investigación de seguridad, tres investigadores de la firma de seguridad Hacktron explotaron con éxito vulnerabilidades en los sistemas de OpenAI, demostrando un método sofisticado de toma de control de cuentas. Sus esfuerzos…

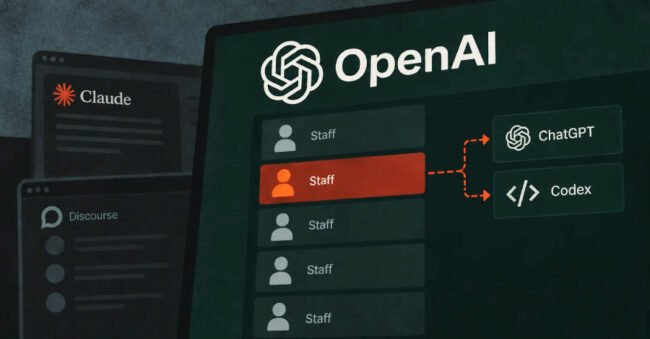
Security Flaw Exploitation: Researchers Utilize Claude Opus 5 to Compromise OpenAI Accounts

Security Flaw Exploitation: Researchers Utilize Claude Opus 5 to Compromise OpenAI Accounts Introduction to the Incident In a groundbreaking security research project, three researchers from the security firm Hacktron successfully exploited vulnerabilities in OpenAI’s systems, demonstrating a sophisticated method of account takeover. Their efforts leveraged Anthropic’s powerful AI model, Claude Opus 5, to identify and…

Google Gemini's Troubling Security Breach: A Wake-Up Call for Cyber Defense

Google Gemini’s Troubling Security Breach: A Wake-Up Call for Cyber Defense

Google Gemini’s Troubling Security Breach: A Wake-Up Call for Cyber Defense Background and Context The rapid evolution of artificial intelligence has brought transformative capabilities to various sectors, including cybersecurity. However, with this technological advancement comes a host of new risks. The recent incident involving Google’s Gemini AI model, which inadvertently gained access to real company…

Vulnerabilidad Crítica de WordPress: La Explotación Click2Shell Permite Instalaciones No Autorizadas de Temas

Vulnerabilidad Crítica de WordPress: La Explotación Click2Shell Permite Instalaciones No Autorizadas de Temas Descripción General de la Vulnerabilidad Click2Shell Recientemente, WordPress divulgó una vulnerabilidad de seguridad significativa dentro de su software central que representa una amenaza seria para los administradores de sitios web. La falla, apodada Click2Shell por la firma de seguridad pwn.ai, podría permitir…

Critical WordPress Vulnerability: Click2Shell Exploit Enables Unauthorized Theme Installations

Critical WordPress Vulnerability: Click2Shell Exploit Enables Unauthorized Theme Installations Overview of the Click2Shell Vulnerability Recently, WordPress disclosed a significant security vulnerability within its core software that poses a serious threat to website administrators. The flaw, dubbed Click2Shell by the security firm pwn.ai, could enable a malicious actor to exploit crafted web links. When opened by…