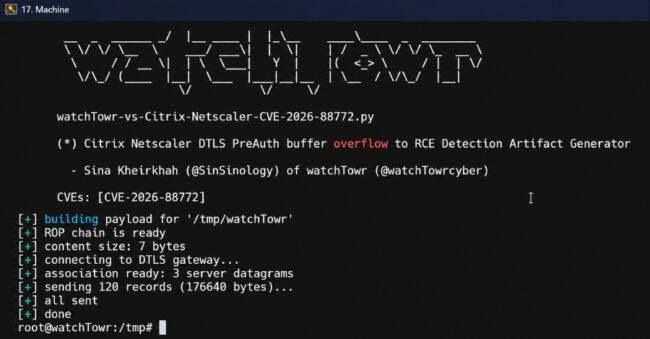
Critical Citrix NetScaler CVE-2026-88772 Vulnerability Exposes Users to Shellcode Execution Risks

Critical Citrix NetScaler CVE-2026-88772 Vulnerability Exposes Users to Shellcode Execution Risks Overview of CVE-2026-88772 A recently disclosed security vulnerability in Citrix NetScaler ADC and Gateway, tracked as CVE-2026-88772, has raised significant alarm among cybersecurity professionals. This critical flaw, which received a high Common Vulnerability Scoring System (CVSS) score of 9.5, is categorized as a memory…
French Tax Data Theft Exposes Vulnerabilities in Cybersecurity Framework

French Tax Data Theft Exposes Vulnerabilities in Cybersecurity Framework

French Tax Data Theft Exposes Vulnerabilities in Cybersecurity Framework Background and Context The recent incident involving the theft of tax data from France’s tax administration has underscored significant vulnerabilities within governmental cybersecurity frameworks. In June and July 2023, attackers exploited stolen passwords belonging to tax administration staff, leading to the unauthorized access and extraction of…

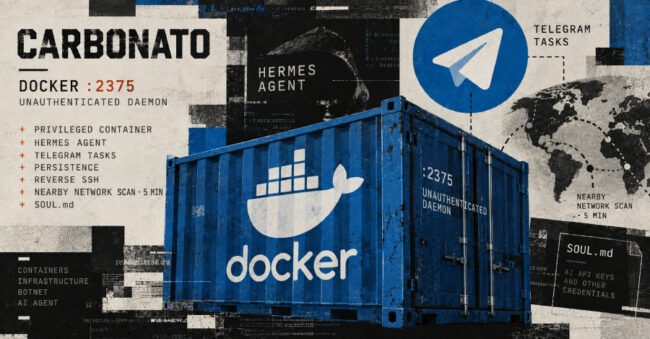
Nuevo Botnet Carbonato Explota Hosts de Docker para Desplegar Agente de IA Hermes Controlado por Telegram

Nuevo Botnet Carbonato Explota Hosts de Docker para Desplegar Agente de IA Hermes Controlado por Telegram Introducción al Botnet Carbonato En un desarrollo preocupante dentro del paisaje de la ciberseguridad, los investigadores han descubierto un nuevo botnet conocido como Carbonato. Este malware demuestra un nivel de operación sofisticado, apuntando a demons Docker de acceso público…

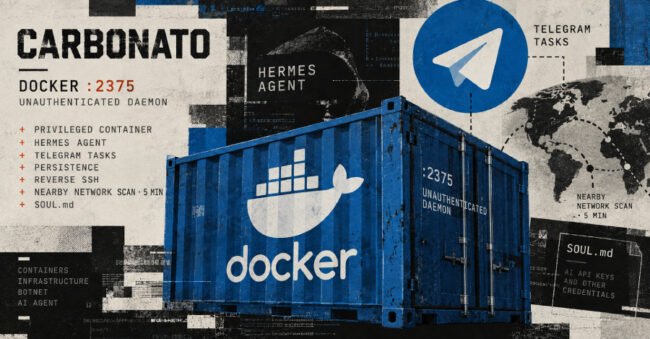
New Carbonato Botnet Exploits Docker Hosts to Deploy Telegram-Controlled Hermes AI Agent

New Carbonato Botnet Exploits Docker Hosts to Deploy Telegram-Controlled Hermes AI Agent Introduction to Carbonato Botnet In a concerning development within the cybersecurity landscape, researchers have uncovered a new botnet known as Carbonato. This malware demonstrates a sophisticated level of operation, targeting publicly accessible Docker daemons to deploy an artificial intelligence (AI) framework called the…

Apple Addresses Critical CoreGraphics Vulnerability with New Security Patches

Apple Addresses Critical CoreGraphics Vulnerability with New Security Patches

Apple Addresses Critical CoreGraphics Vulnerability with New Security Patches Background and Context The recent security update from Apple comes in response to a severe flaw identified as CVE-2026-86950, which affects older versions of iOS, iPadOS, and macOS. This vulnerability is particularly concerning as it has reportedly been exploited in targeted attacks, which is indicative of…

Active Exploitation of SharePoint RCE and MikroTik RouterOS Vulnerabilities: What You Need to Know

Active Exploitation of SharePoint RCE and MikroTik RouterOS Vulnerabilities: What You Need to Know

Active Exploitation of SharePoint RCE and MikroTik RouterOS Vulnerabilities: What You Need to Know Background and Context In the evolving landscape of cybersecurity threats, recent developments have underscored the persistent vulnerabilities present in widely-used software and hardware. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has recently added two critical vulnerabilities to its Known Exploited…

Explotación Masiva de la Vulnerabilidad de Oracle PeopleSoft: Una Amenaza Cibernética Grave

Explotación Masiva de la Vulnerabilidad de Oracle PeopleSoft: Una Amenaza Cibernética Grave Resumen de la Vulnerabilidad Google ha puesto de relieve un resurgimiento de la explotación generalizada que apunta a una vulnerabilidad de seguridad crítica en Oracle PeopleSoft, subrayando la urgencia para que las organizaciones afectadas tomen medidas inmediatas. La vulnerabilidad, identificada como CVE-2026-35273, tiene…

Mass Exploitation of Oracle PeopleSoft Vulnerability: A Severe Cybersecurity Threat

Mass Exploitation of Oracle PeopleSoft Vulnerability: A Severe Cybersecurity Threat Overview of the Vulnerability Google has shed light on a resurgence of widespread exploitation targeting a critical security vulnerability in Oracle PeopleSoft, underscoring the urgency for affected organizations to take immediate action. The vulnerability, identified as CVE-2026-35273, holds a staggering CVSS score of 9.8, categorizing…

Lunex Stealer: A New Threat Leveraging AMD Drivers to Evade Security Measures

Lunex Stealer: A New Threat Leveraging AMD Drivers to Evade Security Measures

Lunex Stealer: A New Threat Leveraging AMD Drivers to Evade Security Measures Background and Context The rise of sophisticated malware has become an alarming trend in the cybersecurity landscape, underscoring the evolving tactics employed by cybercriminals. The recent emergence of the **Lunex Stealer**, a form of malware targeting Ukrainian-speaking users, exemplifies this trend. Discovered by…

Nuevos desarrollos en el malware PamStealer: Persistencia mejorada y descifrado en vivo

Nuevos desarrollos en el malware PamStealer: Persistencia mejorada y descifrado en vivo Descripción general del malware PamStealer PamStealer ha surgido como una amenaza significativa en el ecosistema de macOS, mostrando tácticas avanzadas para comprometer la seguridad del usuario. Originalmente identificado por sus efectivas capacidades de robo de credenciales, el malware ha evolucionado, integrando métodos sofisticados…