Critical APT Vulnerability in Debian and Ubuntu Exposes Users to Man-in-the-Middle Attacks
Overview of the Flaw
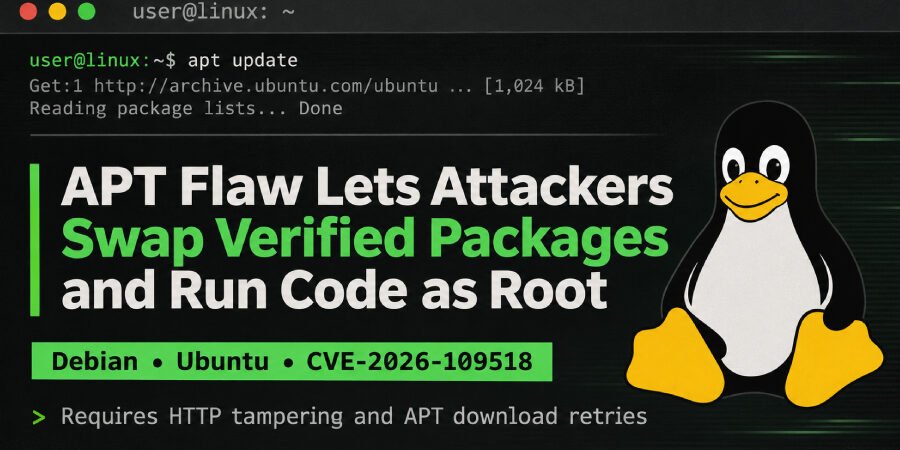
A significant vulnerability has been discovered in the Advanced Package Tool (APT), the package management utility used by Debian and Ubuntu Linux distributions. As outlined in advisories released on November 4 by the developers of Debian, Ubuntu, and APT, this flaw allows a malicious actor to execute a man-in-the-middle (MitM) attack, substituting legitimate packages with compromised versions.
How the Attack Works
The vulnerability arises when APT retries failed download attempts, a feature that is enabled by default in Debian 12 and newer releases. If an attacker is positioned within the network path of a user’s package downloads, they can replace a verified package with a malicious one. Once downloaded and executed, this malicious code can run with root privileges, potentially compromising the entire system.
Potential Implications for Users
- Root Access: Attackers can gain complete control of the system, leading to data theft, system disruption, or the installation of additional malicious software.
- Trust Erosion: Users reliant on Debian and Ubuntu may experience diminished trust in the integrity and security of their package management systems.
- Wider Impact: As these distributions are widely used in both server and desktop environments, the implications could extend beyond individual users to organizations relying on these systems for business-critical applications.
Response from the Community
The Debian and Ubuntu communities have reacted swiftly to the disclosure of this vulnerability. Advisory notices have been disseminated to prompt users and administrators to update their systems as soon as possible. Furthermore, the developers are working on patches and enhancing security features to mitigate the risk of similar vulnerabilities in future releases.
Expert Analysis and Recommendations
Security experts recommend that all users of Debian and Ubuntu check for updates immediately and apply any patches released by their respective distributions. Users should also consider the following best practices:
- Verify Package Sources: Ensure that only trusted and verified repository sources are used for software installations.
- Secure Networks: Employ secure network practices, such as monitoring for unusual activity and using VPNs to enforce encryption against potential MitM attacks.
- Stay Informed: Regularly follow security advisories from Debian, Ubuntu, and other relevant platforms to stay ahead of potential vulnerabilities.
Conclusion
The recently identified APT flaw poses a serious risk for users of Debian and Ubuntu systems, emphasizing the importance of vigilant security practices and timely updates. As the community works to address this vulnerability, it serves as a sobering reminder of the ongoing threats faced in the evolving landscape of cybersecurity.
Source: thehackernews.com