New Corp MDM Spyware Targets Logistics Sector, Compromises SMS and Call Functions
Introduction to Corp MDM Spyware
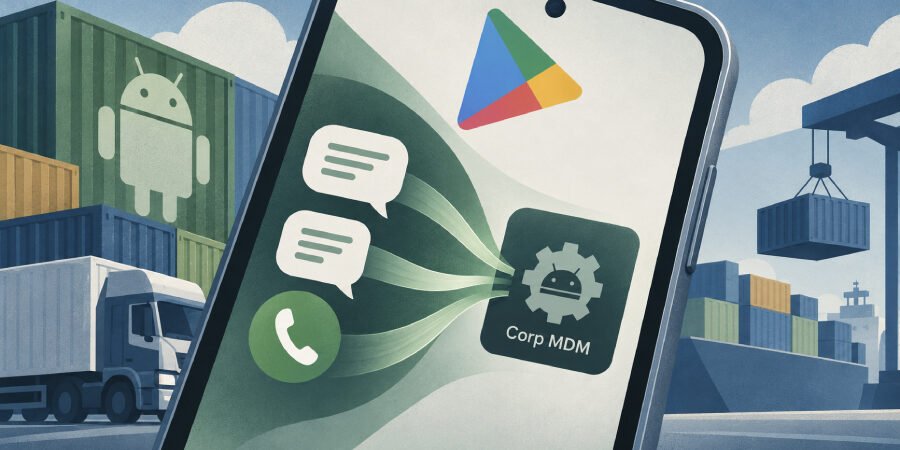
In an alarming trend, the logistics sector has found itself under attack from a sophisticated new spyware dubbed Corp MDM. This malicious software operates primarily on Android devices and introduces a range of security threats by intercepting communications and redirecting calls.
Distribution Methodology
The spyware is being distributed through deceptive means, primarily via counterfeit Google Play pages presenting themselves as legitimate logistics firms, such as CEVA and TKW Logistics. By masquerading as trusted entities, the campaign successfully lures unsuspecting users to download a malicious Android Package Kit (APK) file that is falsely advertised as a system service.
- The app is disguised with the package name “com.corp.mdm”.
- Users may unknowingly install the spyware, believing it to be a necessary tool for their logistics operations.
Technical Features and Functionality
Once installed, Corp MDM spyware quietly operates in the background, allowing attackers to gain unauthorized access to sensitive information and communication channels.
- Stealing new SMS messages: The spyware can capture text messages, potentially revealing sensitive discussions and logistics data.
- Redirecting calls: It can reroute phone calls, allowing cybercriminals to intercept and listen in on discussions relevant to logistics operations.
- Stealth operations: The spyware functions without the user’s awareness, making detection and removal difficult for victims.
Impact on the Logistics Sector
The introduction of Corp MDM spyware poses significant risks to the logistics industry. With the rising adoption of mobile technology in logistics management, the potential for data breaches and operational disruptions increases considerably.
- Data Breaches: Compromised SMS and call intercepts could lead to significant leaks of proprietary information and client data.
- Operational Disruptions: Redirecting calls and stealing messages could hinder timely communication, impacting supply chain operations.
- Trust Erosion: Clients and partners may hesitate to engage with logistics firms known to have been targeted, damaging reputations.
Expert Analysis on Preventive Measures
Experts emphasize the importance of vigilance and proactive measures to combat such threats. Here are some recommended strategies:
- Education and Awareness: Training employees about the risks associated with downloading apps from unofficial sources can significantly reduce the likelihood of infection.
- Use of Mobile Security Solutions: Implementing security software that can detect and neutralize spyware threats on mobile devices is essential.
- Regular Security Audits: Conducting periodic audits of systems and applications can help identify potential vulnerabilities and mitigate risks.
Conclusion
The emergence of Corp MDM spyware underscores the cyber threats that the logistics sector faces in an increasingly digital world. By understanding the methods of distribution and the implications of such threats, firms can better prepare their defenses against this and other malicious software.
Source: thehackernews.com