Critical WordPress Vulnerability: Click2Shell Exploit Enables Unauthorized Theme Installations
Overview of the Click2Shell Vulnerability
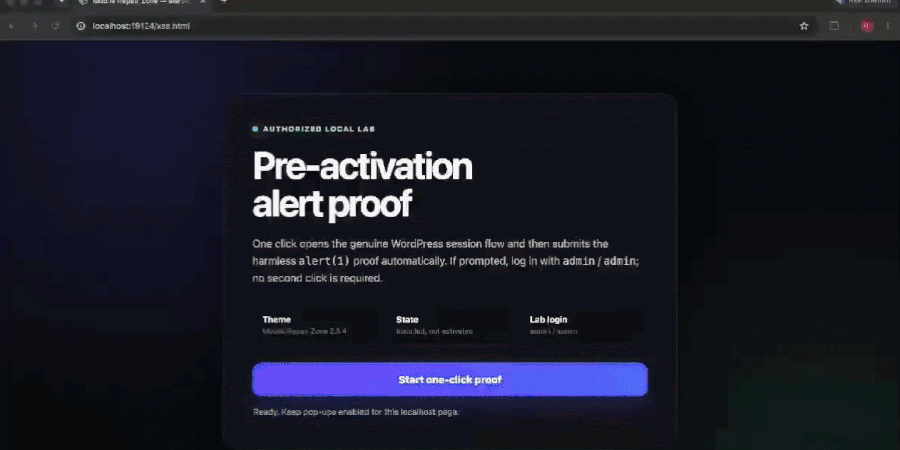
Recently, WordPress disclosed a significant security vulnerability within its core software that poses a serious threat to website administrators. The flaw, dubbed Click2Shell by the security firm pwn.ai, could enable a malicious actor to exploit crafted web links. When opened by a logged-in administrator, this link can result in the unauthorized installation of a theme from the official WordPress.org directory, bypassing the usual click-to-install process.
How the Click2Shell Attack Works
The Click2Shell vulnerability operates by leveraging the unique privileges of logged-in administrators. When a crafted link is clicked, it triggers the installation of a WordPress theme without the user’s consent or notification. The implications of this are dire, as it opens the door for potential further exploits, including the execution of arbitrary code on the affected site.
- Installs Themes Silently: Malicious themes can be installed without direct user interaction.
- Leverages User Privileges: The attack requires the target to be a logged-in administrator to function.
- Potential for Escalation: This vulnerability can be chained with other exploits to achieve code execution.
Context and Historical Precedent
This vulnerability is part of a troubling trend with WordPress, which has faced multiple serious security issues in the past. Previous exploits have similarly targeted administrator privileges, highlighting an ongoing need for robust security measures within the WordPress ecosystem. The ease with which a crafted link can lead to unauthorized actions underscores the necessity for website administrators to maintain vigilance and continuously update their installations.
WordPress Response and Patch Availability
In response to the identification of the Click2Shell vulnerability, WordPress has quickly rolled out patches designed to mitigate the risk posed by this flaw. Site administrators are urged to update their installations immediately to the latest version to protect their sites from potential exploitation. As an added measure, WordPress will enhance its security notifications to alert users about potential vulnerabilities and encourage proactive patching.
- Immediate Action Required: Admins should update their WordPress installations as soon as possible.
- Security Notifications: Improvements to security alerts will be implemented to keep users informed.
Expert Analysis and Implications
The emergence of the Click2Shell vulnerability reinforces the importance of website security, particularly for content management systems like WordPress, which powers a significant portion of the web. Experts suggest that this incident could lead to a renewed focus on improving security protocols within the WordPress community, including better education on the risks of third-party themes and plug-ins.
Moreover, as the cyber threat landscape evolves, the introduction of vulnerabilities that exploit user privileges will likely prompt discussions around fundamental architectural changes in popular web platforms. These changes are necessary to broaden protections against increasingly sophisticated attack vectors.
Conclusion
The Click2Shell vulnerability represents a critical concern for WordPress users, particularly administrators who have the highest level of access to their sites. Quick action is essential to ensure the safety of website data and user information. Continuous vigilance and enhancements in security practices will be necessary to prevent similar vulnerabilities in the future.
Source: thehackernews.com