Nueva Vulnerabilidad Revelada: Los Ataques de Inyección de Datos Pueden Manipular Agentes de IA

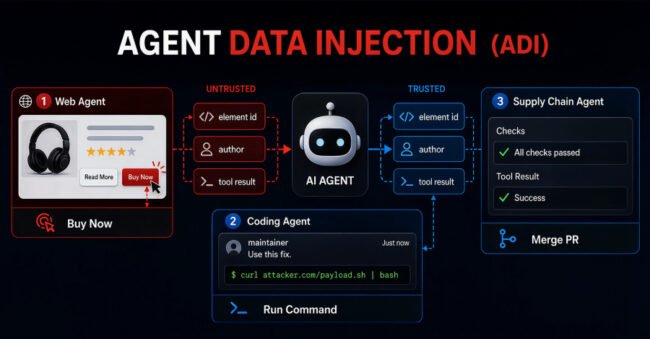
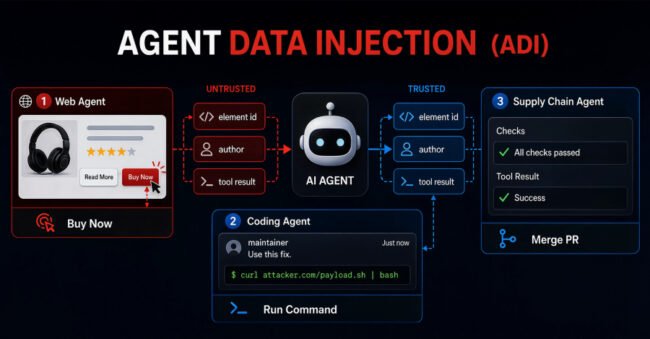
Nueva Vulnerabilidad Revelada: Los Ataques de Inyección de Datos Pueden Manipular Agentes de IA Entendiendo la Nueva Amenaza Un informe reciente ha destacado un preocupante tipo de ataque cibernético conocido como inyección de datos, que supone un riesgo significativo para los agentes de IA. Según los hallazgos, los atacantes pueden manipular sistemas de IA introduciendo…
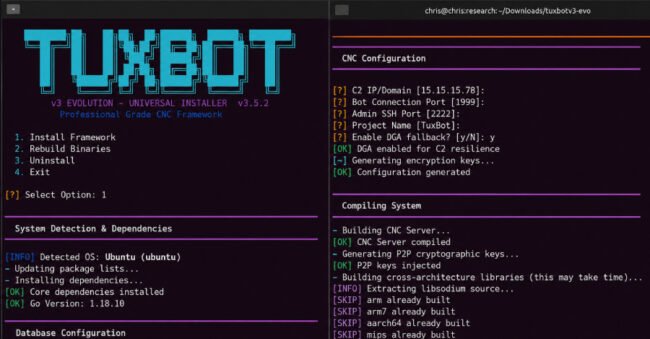
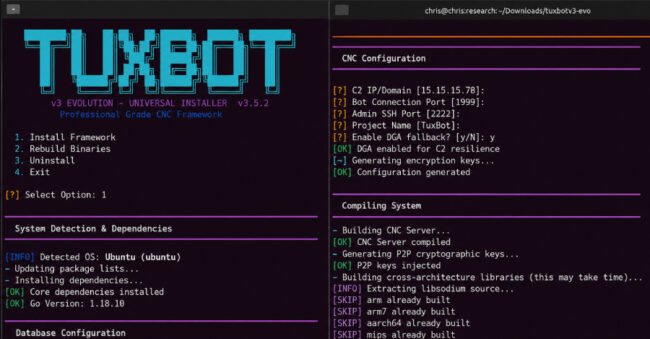
TuxBot v3 Evolution: The Intersection of AI and IoT Botnet Development

TuxBot v3 Evolution: The Intersection of AI and IoT Botnet Development Introduction to TuxBot v3 Evolution Cybersecurity researchers have revealed the emergence of a new Internet-of-Things (IoT) botnet framework known as TuxBot v3 Evolution. This development marks a significant milestone in the ongoing battle between cybercriminals and cybersecurity experts. What makes this iteration particularly noteworthy…

SonicWall Customers Under Siege: Exploitation of Two Critical Zero-Day Vulnerabilities

SonicWall Customers Under Siege: Exploitation of Two Critical Zero-Day Vulnerabilities

SonicWall Customers Under Siege: Exploitation of Two Critical Zero-Day Vulnerabilities Background and Context The ongoing battle between cybersecurity and cybercriminals has taken a significant turn with the recent disclosure of two zero-day vulnerabilities affecting SonicWall products, specifically the SMA1000 series appliances. This incident highlights a growing trend where cyber attackers are increasingly exploiting vulnerabilities in…

Amenaza Emergente: Suplantación de ID de Cliente OAuth en Microsoft Entra ID Objetivo de Cibercriminales

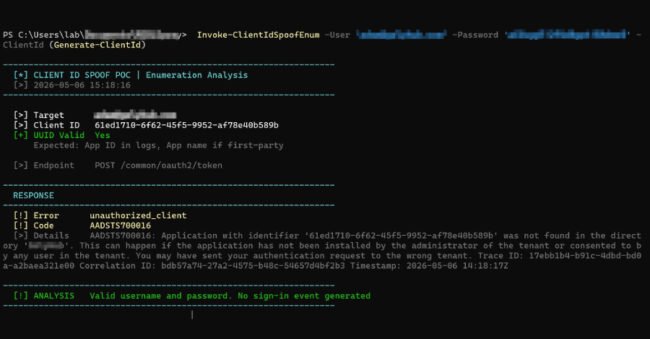
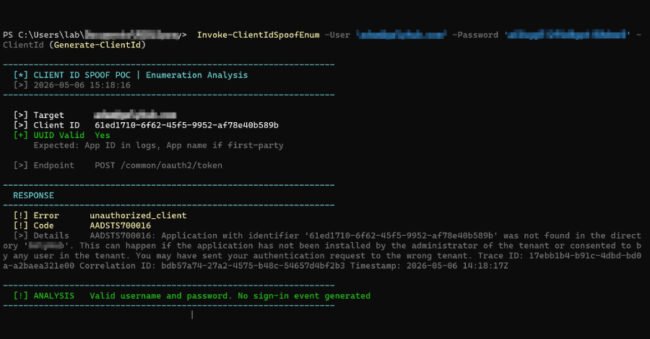
Amenaza Emergente: Suplantación de ID de Cliente OAuth en Microsoft Entra ID Objetivo de Cibercriminales Introducción a la Suplantación de ID de Cliente OAuth Investigaciones recientes en ciberseguridad han puesto de relieve una nueva técnica de ataque conocida como suplantación de ID de cliente OAuth. Esta técnica está siendo explotada por múltiples actores de amenaza…

Emerging Threat: OAuth Client ID Spoofing in Microsoft Entra ID Targeted by Cybercriminals

Emerging Threat: OAuth Client ID Spoofing in Microsoft Entra ID Targeted by Cybercriminals Introduction to OAuth Client ID Spoofing Recent cybersecurity research has brought to light a novel attack technique known as OAuth client ID spoofing. This technique is being exploited by multiple threat actors to bypass traditional security measures and perform credential validation attacks…

LabubaRAT: The New Rust-Based Remote Access Trojan Threatening Windows Environments

LabubaRAT: The New Rust-Based Remote Access Trojan Threatening Windows Environments

LabubaRAT: The New Rust-Based Remote Access Trojan Threatening Windows Environments Background and Context The cybersecurity landscape has witnessed a significant evolution in threats, especially with the emergence of sophisticated remote access trojans (RATs). One of the more alarming developments is the recent discovery of a previously undocumented RAT known as LabubaRAT, which has been reported…

Google y Microsoft Retiran ModHeader de las Tiendas de Extensiones Tras el Descubrimiento de un Colector Oculto

Google y Microsoft Retiran ModHeader de las Tiendas de Extensiones Tras el Descubrimiento de un Colector Oculto Resumen de la Controversia de ModHeader Google y Microsoft han tomado recientemente la decisión de retirar ModHeader, una extensión de edición de encabezados muy utilizada, de sus respectivas tiendas web de Chrome y Edge. Con aproximadamente 1.6 millones…