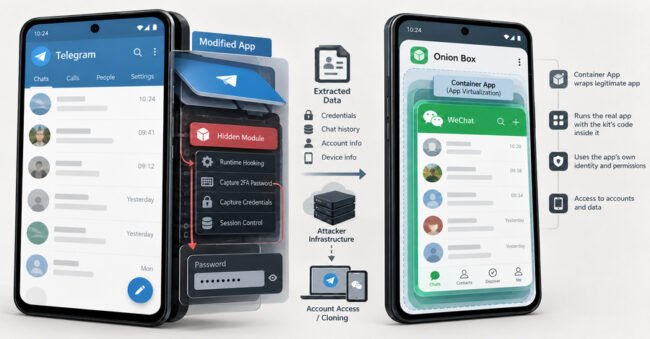
uCreator Android Spyware Representa una Amenaza para los Usuarios de Telegram y WeChat

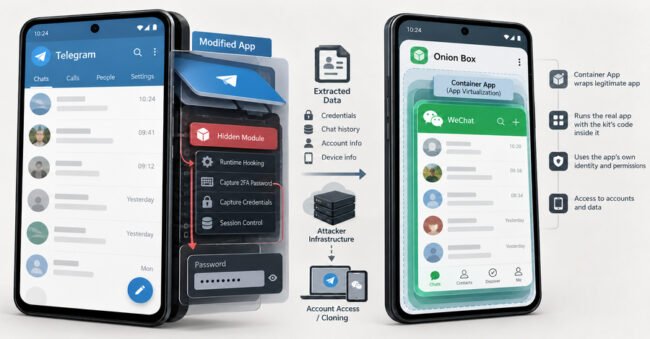
uCreator Android Spyware Representa una Amenaza para los Usuarios de Telegram y WeChat Introducción al Spyware uCreator Investigaciones recientes han revelado la aparición de un sofisticado kit de spyware para Android llamado uCreator, diseñado para secuestrar cuentas de usuarios en plataformas de mensajería populares como Telegram y WeChat. Este software malicioso explota vulnerabilidades al disfrazarse…
uCreator Android Spyware Poses Threat to Telegram and WeChat Users

uCreator Android Spyware Poses Threat to Telegram and WeChat Users Introduction to uCreator Spyware Recent research has revealed the emergence of a sophisticated Android spyware kit named uCreator, designed to hijack user accounts on popular messaging platforms Telegram and WeChat. This malicious software exploits vulnerabilities by disguising itself within modified versions of legitimate applications. As…

Intentos Continuos de Explotación de PHP2Shell Vinculados a Actividades Cibernéticas de Corea del Norte

Intentos Continuos de Explotación de PHP2Shell Vinculados a Actividades Cibernéticas de Corea del Norte Entendiendo la Vulnerabilidad de PHP2Shell PHP2Shell es una shell de comandos basada en la web escrita en PHP que puede facilitar la ejecución de comandos en un servidor comprometido. Su explotación puede llevar al acceso no autorizado y a la manipulación…

Continued PHP2Shell Exploitation Attempts Linked to North Korean Cyber Activities

Continued PHP2Shell Exploitation Attempts Linked to North Korean Cyber Activities Understanding the PHP2Shell Vulnerability PHP2Shell is a web-based command shell written in PHP that can facilitate the execution of commands on a compromised server. Its exploitation can lead to unauthorized access and manipulation of the hosting environment. This vulnerability has been particularly attractive to cybercriminals…

PHP2Shell Exploitation Attempts Intensify Amid Suspected North Korean Cyber Operations

PHP2Shell Exploitation Attempts Intensify Amid Suspected North Korean Cyber Operations

PHP2Shell Exploitation Attempts Intensify Amid Suspected North Korean Cyber Operations Background and Context The cybersecurity community is once again on high alert following the recent revelations concerning the exploitation of the PHP2Shell vulnerabilities, primarily linked to a series of attacks targeting European government agencies. While initial reports from Palo Alto Networks’ Unit 42 suggested these…

El equipo de investigación en seguridad desactiva el actualizador vulnerable de Popcorn Time a través de una masiva campaña de actualización

El equipo de investigación en seguridad desactiva el actualizador vulnerable de Popcorn Time a través de una masiva campaña de actualización Introducción a Popcorn Time y sus amenazas Popcorn Time, una aplicación desde hace mucho abandonada, ganó notoriedad como una plataforma para transmitir películas y programas de televisión pirateados a través de tecnología BitTorrent. Desarrollada…

Security Research Team Disables Vulnerable Popcorn Time Updater Through Massive Update Campaign

Security Research Team Disables Vulnerable Popcorn Time Updater Through Massive Update Campaign Introduction to Popcorn Time and Its Threats Popcorn Time, a long-since-abandoned application, gained notoriety as a platform for streaming pirated movies and TV shows via BitTorrent technology. Developed to provide users with free access to copyrighted content, it quickly became a symbol of…

CISA Flags Critical Vulnerabilities in Collabora Online and Arista VeloCloud: What You Need to Know

CISA Flags Critical Vulnerabilities in Collabora Online and Arista VeloCloud: What You Need to Know

CISA Flags Critical Vulnerabilities in Collabora Online and Arista VeloCloud: What You Need to Know Background and Context The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has recently identified two critical vulnerabilities in widely used software products: Collabora Online and Arista VeloCloud. These vulnerabilities, listed as CVE-2026-110447 and CVE-2026-110448, have been flagged under CISA’s Known…

Investigadores de Seguridad Revelan el Exploit RCE Node2Shell en Node.js a Través de Datos Brotli Manipulados

Investigadores de Seguridad Revelan el Exploit RCE Node2Shell en Node.js a Través de Datos Brotli Manipulados Introducción al Exploit Node2Shell En un desarrollo significativo dentro del panorama de ciberseguridad, investigadores de Imperva han mostrado un alarmante exploit conocido como Node2Shell. Este prueba de concepto explota una falla en la popular plataforma Node.js, permitiendo potencialmente a…