Unraveling the Chrome V8 Zero-Day Exploit: A New Threat to Sandbox Security

Unraveling the Chrome V8 Zero-Day Exploit: A New Threat to Sandbox Security

Unraveling the Chrome V8 Zero-Day Exploit: A New Threat to Sandbox Security Background and Context The cybersecurity landscape is in constant flux, and with that comes an ever-evolving array of vulnerabilities that threaten the integrity of widely-used software. Recently, Google patched a serious vulnerability, identified as CVE-2026-87491, affecting the V8 JavaScript engine within Chrome. This…

Slim Spider: Nuevo Actor de Amenaza Dirigido a Instituciones Financieras Brasileñas y Sistemas de Custodia de Criptomonedas

Slim Spider: Nuevo Actor de Amenaza Dirigido a Instituciones Financieras Brasileñas y Sistemas de Custodia de Criptomonedas Introducción a Slim Spider Un actor de amenaza previamente no documentado, apodado “Slim Spider”, ha surgido como una preocupación significativa de ciberseguridad en Brasil. Desde marzo de 2026, este grupo motivado financieramente ha estado implicado en ataques sofisticados…

Slim Spider: New Threat Actor Targets Brazilian Financial Institutions and Crypto Custody Systems

Slim Spider: New Threat Actor Targets Brazilian Financial Institutions and Crypto Custody Systems Introduction to Slim Spider A previously undocumented threat actor, dubbed “Slim Spider,” has emerged as a significant cybersecurity concern in Brazil. Since March 2026, this financially motivated group has been implicated in sophisticated attacks on Brazilian financial institutions, demonstrating an alarming understanding…

Transforming Intelligence: The CIA's Shift Towards Cyber Operations

Transforming Intelligence: The CIA’s Shift Towards Cyber Operations

Transforming Intelligence: The CIA’s Shift Towards Cyber Operations Background and Context The Central Intelligence Agency (CIA) has long operated at the intersection of human intelligence (HUMINT), signals intelligence (SIGINT), and various other forms of intelligence gathering. However, as the digital landscape evolves, so too does the agency’s operational framework. Recent statements from CIA Deputy Director…

N-able lanza una corrección urgente para una vulnerabilidad crítica de ejecución remota de código (RCE) no autenticada en N-central

N-able lanza una corrección urgente para una vulnerabilidad crítica de ejecución remota de código (RCE) no autenticada en N-central Introducción a la Vulnerabilidad N-able, un jugador prominente en el espacio de monitoreo y gestión remota, ha anunciado el lanzamiento de su cuarta corrección para la plataforma N-central en solo cinco semanas. Esta última actualización aborda…

N-able Releases Urgent Hotfix for Critical Unauthenticated RCE Vulnerability in N-central

N-able Releases Urgent Hotfix for Critical Unauthenticated RCE Vulnerability in N-central Introduction to the Vulnerability N-able, a prominent player in the remote monitoring and management space, has announced the release of its fourth hotfix for the N-central platform within just five weeks. This latest update addresses a critical unauthenticated remote code execution (RCE) vulnerability that…

Cybersecurity Weekly Recap: Chrome 0-Day Vulnerability, Router Hijacks, and Supply Chain Attacks

Cybersecurity Weekly Recap: Chrome 0-Day Vulnerability, Router Hijacks, and Supply Chain Attacks

Cybersecurity Weekly Recap: Chrome 0-Day Vulnerability, Router Hijacks, and Supply Chain Attacks Background and Context In a landscape where cyber threats are becoming increasingly sophisticated, the recent incidents involving a Chrome 0-day vulnerability, router hijacks, and a compromised software supply chain highlight the urgent need for heightened vigilance. The Chrome vulnerability, which exploits a flaw…

Falla de Seguridad Crítica en Routers MikroTik: Los Atacantes Explotan SSH Accesible por Internet para Acceso No Autorizado

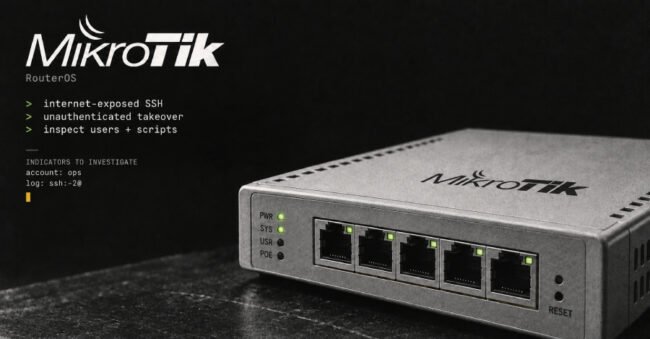
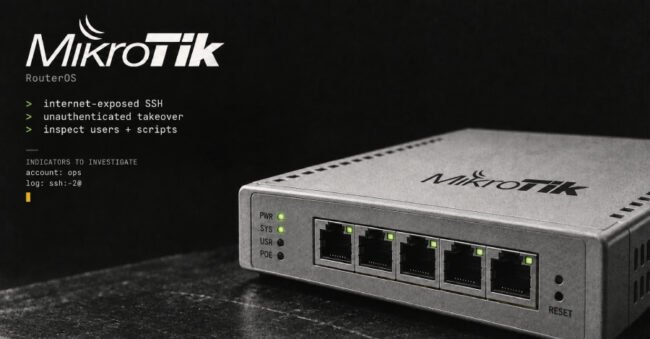
Falla de Seguridad Crítica en Routers MikroTik: Los Atacantes Explotan SSH Accesible por Internet para Acceso No Autorizado Descripción General de la Vulnerabilidad El 5 de septiembre, CERT Polska emitió una advertencia sobre una grave vulnerabilidad de seguridad que afecta a los routers MikroTik. La falla se centra en el servicio de acceso remoto Secure…

Critical Security Flaw in MikroTik Routers: Attackers Exploit Internet-Accessible SSH for Unauthorized Access

Critical Security Flaw in MikroTik Routers: Attackers Exploit Internet-Accessible SSH for Unauthorized Access Overview of the Vulnerability On September 5, CERT Polska issued a warning regarding a serious security vulnerability affecting MikroTik routers. The flaw centers around the routers’ Secure Shell (SSH) remote-access service, which is exposed to the internet and can be exploited by…

Exploiting the Unprotected: The MikroTik Router SSH Hijack Incident

Exploiting the Unprotected: The MikroTik Router SSH Hijack Incident

Exploiting the Unprotected: The MikroTik Router SSH Hijack Incident Background and Context The recent alarm raised by CERT Polska regarding the exploitation of MikroTik routers has revealed a significant vulnerability within the cybersecurity landscape. As remote work becomes increasingly prevalent, the reliance on routers for secure connectivity has surged. MikroTik, a provider known for its…