OpenRouter Discontinues Partnerships with Three AI Providers Following Data Theft Revelations
Overview of the Incident
In a startling revelation, the industrial cybersecurity firm Dragos reported that attackers had been siphoning data from three major AI inference providers for several months. Alarmingly, the targeted hosting firms were completely unaware of the breach until informed by Dragos researchers. This incident raises significant concerns regarding data security in the burgeoning field of artificial intelligence.
The Nature of the Breach
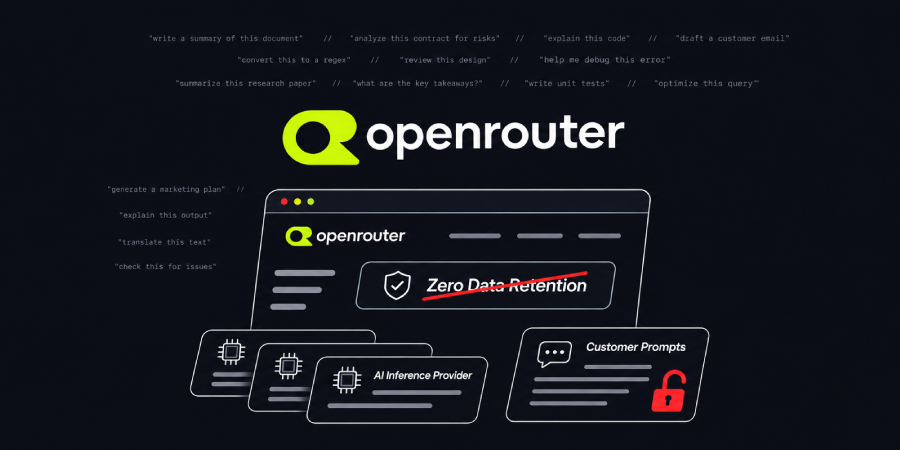
The stolen data included prompts flagged as “Zero Data Retention,” a setting that ideally ensures that any query made by users is not stored or retrievable. This indicates not only a severe lapse in security protocols at the affected providers but also highlights the potential risks associated with AI systems that claim to prioritize user privacy.
OpenRouter’s Response
As a direct consequence of the data theft, OpenRouter has made the decisive move to drop its relationships with the three affected AI providers. OpenRouter, which serves as a gateway for customers’ AI requests to a diverse pool of providers, is emphasizing its commitment to safeguarding user data amid these alarming circumstances.
Implications for the AI Industry
The implications of this breach are profound. As AI technologies become more prevalent in various industries, the vulnerability of proprietary data grows. This breach not only undermines trust in AI hosting firms but also serves as a critical reminder of the need for stringent cybersecurity measures. Industry experts warn that without robust security protocols, firms may face long-term reputational damage and potential legal ramifications.
Expert Analysis and Recommendations
Cybersecurity analysts highlight several key recommendations for AI companies looking to bolster their defenses against such breaches:
- Implement Advanced Threat Detection: AI providers are encouraged to adopt more sophisticated threat detection systems to identify intrusion attempts quickly.
- Regular Security Audits: Conducting frequent security assessments will help identify vulnerabilities before they can be exploited by malicious actors.
- Enhance Data Privacy Protocols: Providers need to reassess and enhance existing data retention policies to ensure compliance with privacy standards.
- Transparency with Users: Building trust through transparency about data security practices is essential for retaining user confidence in AI services.
Conclusion
The recent data breach affecting three AI inference providers serves as a critical wake-up call for the entire tech industry. As the reliance on AI continues to grow, so does the need for rigorous security measures. OpenRouter’s decision to sever ties with the compromised firms underscores the profound responsibility that service providers have to protect user data and maintain public trust in AI technologies.
Source: thehackernews.com