Major Security Flaw Exposed: Default Passwords in Car Apps Allow Full Access to Vehicles
Introduction to the Vulnerability
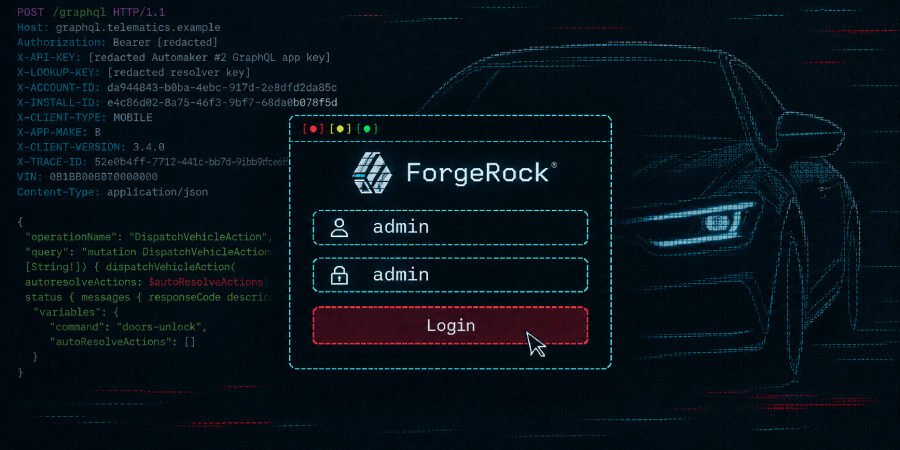
In a shocking revelation, security researchers have uncovered a critical vulnerability affecting the mobile applications of two well-known automakers. The issue lies in the flawed login systems that allow unauthorized access to customer accounts and vehicles, potentially putting owners at risk. The root of the problem is a default password, ‘admin:admin’, still present on servers managed by ForgeRock, an identity management platform now part of Ping Identity.
How the Exploit Works
The researchers demonstrated how easy it was to gain full access to customer accounts through the mobile apps. By exploiting the default credentials found on the ForgeRock servers, they were able to:
- Sign into any customer account without permission.
- Unlock car doors remotely.
- Start the engine of connected vehicles.
This level of access raises severe security concerns, emphasizing the importance of stringent password management practices across all platforms, especially those connected to personal and sensitive assets like vehicles.
Implications for Consumers and Automakers
The implications of this breach are far-reaching. For consumers, the risk of vehicle theft and unauthorized access to personal information is now more pronounced. For automakers, the incident raises serious questions about their IT security practices and their commitment to protecting customer data. The situation could lead to:
- A loss of consumer trust in connected vehicle technologies.
- Increased scrutiny from regulatory bodies regarding data protection.
- A potential financial fallout due to recalls and enhanced security measures.
As vehicles become increasingly interconnected, automakers must prioritize cybersecurity as robustly as they do physical safety features.
The Role of ForgeRock and Ping Identity
ForgeRock, a platform responsible for identity and access management, is now under the scrutiny of security experts following this breach. With its integration into Ping Identity, the situation becomes more complex, as consumers and businesses rely on these platforms for security protocols. Experts argue that such critical lapses could have cascading effects on similar identity management systems across various industries.
Expert Opinions on the Issue
Cybersecurity experts have weighed in on the significance of this breach, with many emphasizing that default passwords should never be present in production environments. According to Dr. Jane Holloway, a cybersecurity analyst:
“This incident highlights an alarming oversight in cybersecurity protocols. Default passwords are a well-known vulnerability, yet they persist in too many systems. Organizations must take proactive steps to secure their user accounts.”
Such statements reflect a consensus in the cybersecurity community that organizations need to enforce stricter security measures and regular audits to mitigate risks.
Conclusion
The discovery of the default ‘admin:admin’ password leading to major vulnerabilities in the mobile apps of two automakers serves as a wake-up call for the automotive industry. As connected cars become more prevalent, ensuring robust cybersecurity measures is essential to protect both consumer data and vehicle integrity. Automakers and service providers must learn from this incident and implement stronger security protocols to avoid similar breaches in the future.
Source: thehackernews.com