Google’s Takedown of a 1.3 Million-Device Android Botnet: Unpacking the Alarming Implications
Background and Context
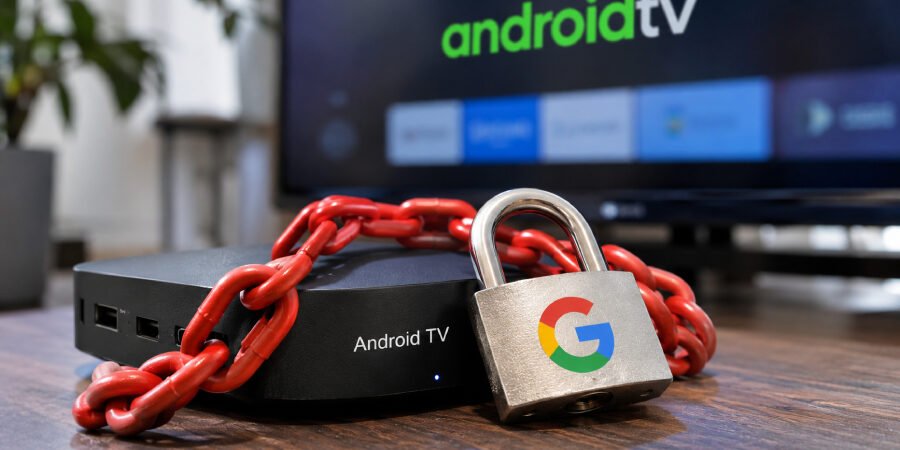
In late October 2023, Google executed a significant operation that dismantled a **botnet** comprising over 1.3 million compromised Android devices, primarily TV set-top boxes. This event stands as a stark reminder of the vulnerabilities present in Internet of Things (IoT) devices, particularly those that are often overlooked due to their benign appearances. The incident also sheds light on a troubling trend where manufacturers may deliberately compromise device security for profit. In this case, the Chinese firm **Videostrong** is accused of embedding a backdoor into its devices, which allowed cybercriminals to exploit the hardware for activities like ad fraud and unauthorized internet traffic routing.
This incident is not isolated; it resonates with previous high-profile botnet disruptions such as the **Mirai botnet**, which similarly exploited IoT vulnerabilities to launch large-scale Distributed Denial of Service (DDoS) attacks. The Mirai botnet’s legacy continues to cast a long shadow over the cybersecurity landscape, serving as a cautionary tale of how unsecured devices can be repurposed for malicious intents. As we increasingly integrate smart devices into our daily lives, the implications of such security failures become more pronounced, emphasizing the urgent need for increased scrutiny in device manufacturing and software development practices.
Moreover, the timing of this disruption is critical as it arrives amidst growing concerns over cybersecurity and the threat of large-scale attacks on infrastructure. With more consumers purchasing IoT devices during holiday sales, the potential for compromised devices to be introduced into homes increases. The ongoing evolution of cyber threats necessitates that both consumers and manufacturers take proactive measures to safeguard against exploitation, making this recent takedown a crucial wake-up call.
Technical Analysis
At the core of this botnet’s operation was the exploitation of **backdoor access** embedded by Videostrong in its set-top boxes. A backdoor is a method of bypassing normal authentication procedures, allowing unauthorized access to the device. In this particular case, the backdoor enabled cybercriminals to control the devices remotely, resulting in a vast network of compromised systems that could be weaponized for nefarious purposes. These devices were primarily leveraged for **ad fraud**, where automated processes would generate revenue for the attackers by simulating legitimate user activity.
The malware utilized in this botnet was sophisticated enough to facilitate the interception of internet traffic, effectively turning compromised set-top boxes into **proxy servers**. This method not only obscured the identities of the attackers but also risked exposing unsuspecting users to potential data breaches and privacy violations. The scale of this operation—over 1.3 million devices—highlights a serious gap in the security protocols for consumer electronics, particularly those that prioritize cost over security features.
Additionally, the operation of this botnet serves as a reminder of the fragility of device ecosystems. The reliance on third-party applications and services means that vulnerabilities can be introduced at multiple points, often without the end user being aware. The complexity of modern operating systems, combined with inadequate security measures, creates a fertile ground for exploits that can have far-reaching consequences.
Scope and Real-World Impact
The impact of this Android botnet disruption is significant, affecting not just the immediate users of the compromised devices but also the broader internet infrastructure. With over 1.3 million devices taken offline, the potential for a reduction in fraudulent ad activities is a positive outcome; however, the incident raises questions about the security of similar devices worldwide. Many users may remain unaware of the vulnerabilities present in their own devices, leaving them exposed to future attacks.
Comparatively, the 2016 Mirai botnet attack leveraged compromised IoT devices to launch one of the largest DDoS attacks in history, affecting major services like **Dyn DNS** and disrupting access to sites like Twitter and Netflix. The similarities between these incidents underscore the ongoing risks associated with IoT devices, suggesting that without significant changes in manufacturing practices, history is likely to repeat itself.
Countries with high penetration of IoT devices, particularly in North America and Asia, are at greater risk of similar attacks. The potential for compromised devices to be used as a conduit for larger cyber attacks poses a serious threat to both individual privacy and corporate networks, making it imperative for stakeholders to take action.
Attack Vectors and Methodology
The methodology behind this botnet operation involved several key steps:
- Device Compromise: Videostrong embedded a backdoor during the manufacturing process, allowing for unauthorized access.
- Remote Control: Cybercriminals used the backdoor to remotely control the devices, effectively converting them into a botnet.
- Ad Fraud Execution: The compromised devices were leveraged to generate fraudulent ad clicks, maximizing revenue for the attackers.
- Traffic Routing: The botnet was used to route internet traffic through the compromised devices, obscuring the attackers’ identities.
- Network Expansion: The botnet’s capabilities allowed it to grow by potentially recruiting additional devices through similar vulnerabilities.
Mitigation and Defense Recommendations
To mitigate the risks associated with compromised devices and similar botnets, both system administrators and end users should take proactive measures. Recommendations include:
- Firmware Updates: Regularly update the firmware of all IoT devices to ensure the latest security patches are applied.
- Device Configuration: Change default passwords and settings to reduce the chances of unauthorized access.
- Network Segmentation: Isolate IoT devices on a separate network to limit potential exposure to the main network.
- Use Security Solutions: Implement network security solutions that can detect and block suspicious activity associated with botnets.
- Educate Users: Raise awareness about the risks associated with IoT devices and promote best practices for securing them.
Industry Implications and Expert Perspective
The long-term implications of this incident are profound. As IoT devices continue to proliferate, manufacturers will face increased scrutiny regarding their security practices. Experts predict that this disruption will spur regulatory discussions around standards for device security, as consumers demand greater accountability from manufacturers. The cybersecurity landscape may also shift as companies invest more heavily in security measures to prevent similar incidents, potentially leading to a more robust security framework within the IoT sector.
Furthermore, the rise of cybercriminal networks that exploit such vulnerabilities highlights the need for a multi-faceted approach to cybersecurity. Collaboration between manufacturers, cybersecurity firms, and regulatory bodies will be essential to address the challenges posed by increasingly sophisticated threats. The incident serves as a rallying cry for stakeholders to prioritize security through proactive measures, from the design phase right through to consumer education.
Conclusion
The takedown of the 1.3 million-device Android botnet by Google highlights the pressing need for improved security practices within the IoT sector. As we increasingly rely on smart devices, the risks associated with compromised hardware will only grow. The implications of this incident extend beyond immediate financial losses from ad fraud; they pose a significant threat to user privacy and network integrity.
As we reflect on the lessons learned from this incident, it is clear that both consumers and manufacturers must prioritize security. The ongoing evolution of cyber threats necessitates a proactive approach to safeguarding devices, ensuring that the convenience of modern technology does not come at the cost of security. The future of IoT security hinges on collaboration, transparency, and commitment to best practices across the industry.
Original source: thehackernews.com