NetamLoader Malware: A Sophisticated Threat to Asian Government Systems
Background and Context
In an alarming development that underscores the growing sophistication of cyber threats, Kaspersky has recently disclosed details about a malware strain dubbed **NetamLoader**, which specifically targets government organizations across Asia. This malware exploits a custom build of Windows 10 employed exclusively by government entities, raising serious concerns about national security, data integrity, and the vulnerabilities of critical infrastructure. Historically, government systems have been prime targets for cybercriminals, especially in regions with heightened geopolitical tensions. The emergence of NetamLoader adds another layer of complexity to an already challenging cybersecurity landscape.
The timing of this discovery is particularly significant as it follows a series of high-profile cyberattacks that have exploited similar vulnerabilities in government systems. For instance, the 2020 SolarWinds attack revealed the extensive risks associated with supply chain vulnerabilities, where attackers infiltrated networks through trusted software updates. Similarly, the targeting of government entities by advanced persistent threat (APT) groups has become commonplace, with numerous incidents reported over the past few years. This trend raises critical questions about the readiness of governmental cybersecurity measures and the effectiveness of existing protocols.
As governments increasingly rely on technology to manage operations, the implications of malware like NetamLoader extend beyond immediate data breaches. The potential for leaking sensitive information or disrupting essential services could have cascading effects, prompting a reevaluation of cybersecurity strategies across the region. The focus on government systems is not merely about theft; it is about undermining public trust and destabilizing political landscapes.
Technical Analysis
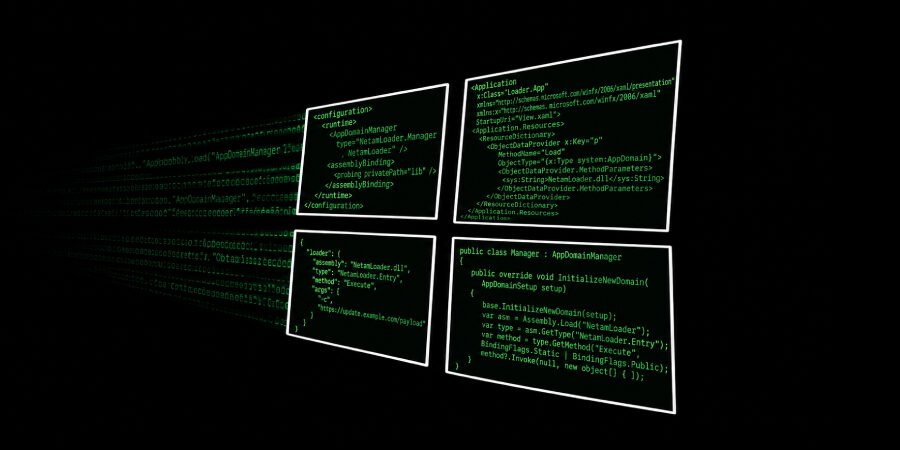
NetamLoader employs a **sophisticated infection chain** that leverages a previously undocumented **.NET assembly-loading framework**, which allows it to manipulate and execute code within the .NET environment effectively. This framework enables the malware to load additional payloads while remaining stealthy, making detection challenging for traditional security solutions. The use of .NET technology is particularly concerning, as it is foundational to many applications within government systems, providing a robust attack surface for malicious actors.
The mechanism of action for NetamLoader unfolds through a series of calculated steps. Initially, the malware infiltrates the system, often through phishing emails or compromised third-party software. Once inside, it utilizes the custom Windows 10 build’s inherent features, executing its payloads in a manner that bypasses standard security measures. The **.NET injection** technique allows it to dynamically load libraries without raising red flags, making it difficult for security teams to ascertain the presence of malicious code.
Moreover, NetamLoader’s ability to adapt and evolve poses a significant challenge for cybersecurity professionals. As it continues to develop, the malware could potentially incorporate more advanced evasion techniques, including polymorphic code that changes with each execution. This ongoing evolution demands constant vigilance and an agile response from security teams, emphasizing the need for proactive rather than reactive defense measures.
Scope and Real-World Impact
The immediate impact of NetamLoader is evident across various government organizations in Asia, particularly those managing sensitive data and critical infrastructure. While Kaspersky has not disclosed the specific countries affected, the implications are broad, suggesting a targeted approach that could lead to significant data breaches and operational disruptions. Comparatively, this incident mirrors past attacks on governmental systems, such as the 2015 OPM breach in the United States, where attackers accessed sensitive information on millions of federal employees, leading to long-lasting ramifications.
The compromised data in this latest incident could range from personal identifiable information (PII) to classified government documents, potentially exposing state secrets or sensitive intelligence. The ramifications extend beyond data loss; they can result in compromised national security, public trust erosion, and even geopolitical tensions. As governments begin to assess the fallout, the urgency for enhanced cybersecurity measures becomes apparent.
Attack Vectors and Methodology
The attack methodology employed by NetamLoader can be broken down into several key stages:
- Initial Compromise: Attackers typically gain access via phishing emails containing malicious attachments or links, or through exploited vulnerabilities in third-party software.
- Execution: Once the malware is deployed, it utilizes the custom Windows 10 build to execute its payloads unobtrusively, often employing .NET injection techniques.
- Data Exfiltration: The malware may establish communication with remote servers to exfiltrate sensitive data, while employing encryption to obfuscate its activities.
- Persistence: NetamLoader implements methods to ensure it remains entrenched within the system, often modifying system settings or deploying additional malware components.
Mitigation and Defense Recommendations
To safeguard against threats like NetamLoader, organizations should adopt a comprehensive cybersecurity strategy that includes:
- Regular Updates: Ensure all software, particularly operating systems and applications, are kept up-to-date with the latest security patches.
- Employee Training: Conduct regular cybersecurity awareness training to educate employees about phishing attacks and safe browsing practices.
- Advanced Threat Detection: Implement advanced threat detection solutions that utilize behavioral analysis and machine learning to identify suspicious activities.
- Incident Response Plan: Develop and regularly update an incident response plan to quickly address any breaches or anomalies detected within the system.
Industry Implications and Expert Perspective
The emergence of NetamLoader signifies a troubling trend in the escalation of cyber threats targeting government entities. Experts suggest that these types of attacks are becoming more frequent and sophisticated, necessitating a shift in the cybersecurity paradigm. As nation-states increasingly engage in cyber warfare, the lines between criminal and state-sponsored activities blur, leading to heightened risks for government systems worldwide.
The long-term implications for the cybersecurity industry include a potential reevaluation of frameworks and policies governing data protection and privacy. Organizations may need to invest more heavily in cybersecurity infrastructure and training, particularly in regions with higher risks of state-sponsored attacks. Additionally, as cyber threats evolve, collaboration among international cybersecurity agencies will be crucial in developing effective countermeasures and sharing intelligence.
Conclusion
NetamLoader represents more than just another malware strain; it embodies the escalating threats that governments face in an interconnected world. As cybercriminals devise increasingly sophisticated methods to infiltrate secure systems, the necessity for robust cybersecurity measures becomes clear. The lessons learned from this incident will not only shape future responses to cyber threats but also influence how governments and organizations prioritize their cybersecurity strategies moving forward.
The unfolding narrative surrounding NetamLoader serves as a stark reminder of the vulnerabilities that persist within even the most secure systems. As we advance into an era defined by digital transformation, it is imperative that both public and private sectors remain vigilant, adaptive, and proactive in their defense against the ever-evolving landscape of cyber threats.
Original source: thehackernews.com