WordPress Addresses Critical Vulnerability Allowing Potential Code Execution
Overview of the Vulnerability
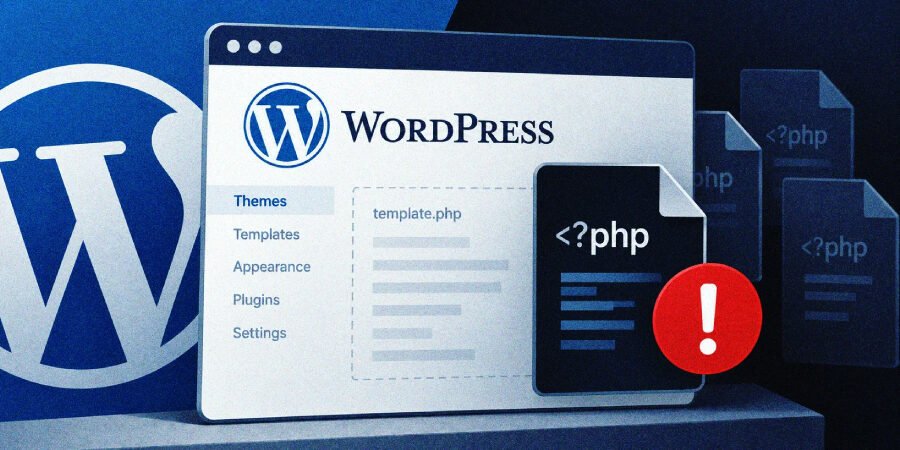
WordPress, a leading content management system that powers over 40% of the web, has recently released a patch for a significant flaw found in its core software. Discovered on September 22, 2026, in version 7.1.2, the issue allows an unauthenticated attacker to load a PHP file from outside of a site’s theme folders. This flaw poses a serious security risk as it could enable the attacker to execute arbitrary code on certain server configurations.
Technical Details of the Flaw
The core vulnerability stems from how WordPress processes file paths, specifically the loading of PHP files. When manipulated carefully, the flaw allows attackers to target specific servers that are misconfigured or have weak security measures in place. Here are the main technical insights:
- Unauthenticated Access: Attackers do not require any user account to exploit this vulnerability, making it particularly dangerous.
- Sever Configuration Dependency: The success of the exploit largely depends on server settings that allow PHP execution from outside theme folders.
- Impact Scope: The flaw affects all supported versions of WordPress, including those dating back to version 4.7, emphasizing the importance of timely updates.
Implications for Site Owners
The potential consequences of this critical vulnerability are alarming for website owners relying on WordPress for their online presence. An exploited vulnerability might lead to unauthorized access, data breaches, or even complete site takeover. Therefore, the response to this vulnerability must be swift and thorough. Key implications include:
- Urgent Updates Required: Site administrators are encouraged to upgrade to version 7.1.2 or later to mitigate this risk.
- Potential for Data Breaches: Attackers could exploit the flaw to access sensitive data, posing risks to both the website owners and their users.
- Increased Security Measures: The vulnerability serves as a reminder for all site owners to review and enhance their security practices, including server configurations and the use of security plugins.
Expert Analysis
Cybersecurity experts have weighed in on the implications of this vulnerability, highlighting both the immediate concerns and potential long-term impacts on the WordPress ecosystem. Notable points include:
- Community Response: The rapid release of the patch demonstrates the commitment of the WordPress community to security, but it also raises questions about the testing processes in place for earlier releases.
- Evolving Threat Landscape: As WordPress continues to expand, so does its attractiveness as a target for attackers. This incident emphasizes the need for ongoing vigilance and improvement in security protocols.
- Importance of User Education: Site owners must be educated on the significance of timely updates and proactive security measures to safeguard their websites against similar vulnerabilities in the future.
Conclusion
The recent patch issued by WordPress addresses a critical vulnerability that could have severe consequences if left unmitigated. As the platform continues to be a foundational tool for millions of websites, ongoing security improvements and user education will be crucial in combating the evolving threat landscape. Administrators are urged to update their installations promptly and review their security practices to prevent possible exploitation.
Source: thehackernews.com