CyberStrikeAI: The Rise of AI-Driven Cyber Attacks Against Japan
Background and Context
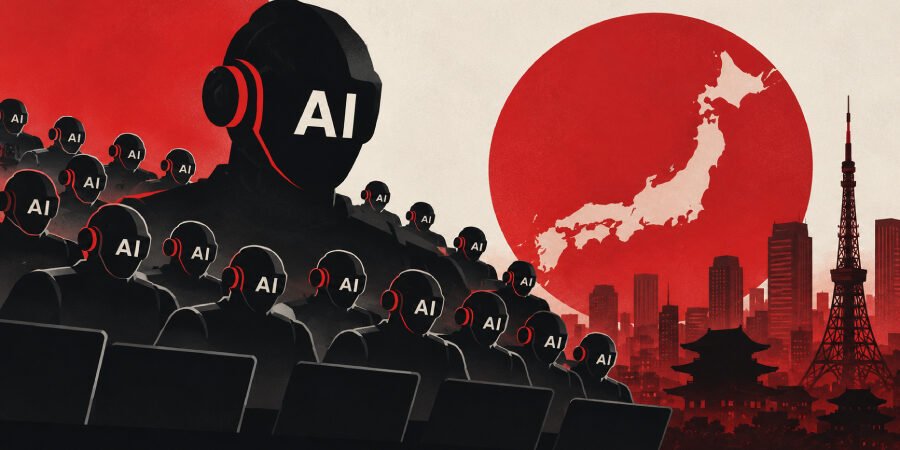
The recent disclosure of cyber attacks employing artificial intelligence (AI) to orchestrate hacking operations against Japanese organizations has sent ripples through the cybersecurity landscape. Cybersecurity researchers from TrendAI uncovered that the attackers utilized a network of 44 AI agents to automate and enhance their malicious activities. This innovative approach marks a significant shift in cyber attack methodologies, moving from human-centric operations to a more autonomous, machine-driven model. Such developments raise critical questions about the future of cybersecurity and the potential vulnerabilities that lie in the adoption of AI technologies.
Historically, Japan has been a frequent target for cyber threats, particularly due to its status as a global economic powerhouse and a hub for technological innovation. Previous incidents, such as the 2019 attack on Japan’s Ministry of Defense and the 2020 cyber intrusion affecting the Tokyo Olympics, underscore the persistent risks faced by organizations in the region. However, the integration of AI into these operations represents a new frontier in cybercrime, showcasing adversaries’ ability to leverage cutting-edge technologies to amplify their offensive capabilities.
The implications of AI-enhanced cyber attacks extend beyond immediate operational impacts; they challenge the foundational assumptions of cybersecurity as we know it. As AI becomes increasingly accessible, both to legitimate enterprises and malicious actors, the traditional methods of defense may struggle to keep pace. This convergence of technology and crime is not merely an escalation but rather a transformative shift that could redefine the threat landscape, making it imperative for organizations to reassess their cybersecurity strategies.
Technical Analysis
The technical architecture of CyberStrikeAI’s operations reveals a sophisticated and automated framework. Utilizing 44 AI agents, the attackers were able to execute a range of malicious tasks, including reconnaissance, vulnerability scanning, and even exploitation of identified weaknesses. Each agent was likely programmed to handle specific aspects of the attack lifecycle, allowing for parallel processing and a significantly reduced time to breach defenses. This orchestration of AI agents is reminiscent of swarm intelligence, where multiple entities work collectively towards a common goal, thereby increasing efficiency and speed.
The AI agents function through machine learning algorithms that enable them to adapt to the environment and the security measures in place. By analyzing patterns, these agents can identify vulnerabilities that may not be immediately obvious to human operators. They can also simulate human-like decision-making processes, allowing for more nuanced and stealthy approaches to various targets. This level of sophistication not only increases the likelihood of successful infiltration but also complicates detection efforts by traditional security measures.
Moreover, the use of AI in cyber attacks highlights a critical evolution in the tactics employed by cybercriminals. Rather than relying solely on brute force attacks or simple phishing schemes, adversaries can now orchestrate multi-faceted operations that require significantly fewer human resources. This shift may lead to an increase in the frequency and severity of cyber incidents, as the barrier to entry for conducting sophisticated attacks lowers, enabling even less skilled actors to leverage powerful AI tools.
Scope and Real-World Impact
The attacks orchestrated by CyberStrikeAI have raised alarms not only within Japan but also among international cybersecurity communities. Organizations targeted included key infrastructure entities, financial institutions, and technology firms, all critical to the nation’s economy and security. The potential fallout from such attacks could involve sensitive data breaches, financial losses, and disruptions to essential services, reminiscent of the 2017 WannaCry ransomware attack that affected organizations worldwide, including critical infrastructure in Japan.
As these incidents unfold, the real-world impact can be profound. Cybersecurity experts warn that the ability to automate hacking operations could lead to an increase in cyber espionage and sabotage, with ramifications extending beyond Japan. The interconnectedness of global supply chains means that disruptions in one region can have cascading effects across multiple sectors worldwide.
Attack Vectors and Methodology
- Reconnaissance: AI agents perform scans to gather intelligence on target networks, identifying weaknesses and entry points.
- Exploitation: Utilizing automated scripts, agents exploit vulnerabilities discovered during reconnaissance.
- Data Exfiltration: Once inside, the agents systematically gather sensitive data, employing obfuscation techniques to evade detection.
- Persistence: AI agents implement mechanisms to maintain access, ensuring continued control over compromised systems.
- Covering Tracks: Finally, the agents erase logs and alter configurations to prevent detection and analysis of the attack.
Mitigation and Defense Recommendations
- Implement AI-Powered Defense Tools: Utilize advanced security solutions that leverage AI to identify and respond to threats in real-time.
- Regular Vulnerability Assessments: Conduct frequent assessments to identify and remediate weaknesses in systems before they can be exploited.
- Employee Training: Train staff to recognize phishing attempts and suspicious activities, focusing on human factors that could aid in detection.
- Incident Response Plans: Develop and regularly update incident response plans to ensure preparedness against AI-driven attacks.
- Network Segmentation: Segment networks to limit the potential impact of a breach, isolating critical systems from less secure environments.
Industry Implications and Expert Perspective
The emergence of AI-driven cyber attacks signifies a pivotal moment for the cybersecurity industry. Experts warn that as adversaries become more adept at leveraging AI, organizations must evolve their defensive strategies accordingly. The growing threat landscape may necessitate a shift towards more proactive and adaptive security measures rather than reactive ones. This could involve increased collaboration among cybersecurity professionals, sharing intelligence and resources to build a more resilient defense against sophisticated threats.
Furthermore, regulatory bodies may need to implement stricter guidelines and frameworks regarding the use of AI in both cyber operations and defense strategies. This evolution in the regulatory landscape could shape how organizations allocate resources towards cybersecurity, emphasizing the need for innovative solutions that can counteract AI-enhanced threats.
Conclusion
The recent cyber attacks utilizing CyberStrikeAI’s network of AI agents represent a significant evolution in the tactics employed by cybercriminals. As organizations grapple with the implications of these developments, it is crucial to recognize that the integration of AI into cyber attacks not only complicates the threat landscape but also poses a serious challenge to existing defense mechanisms. The need for adaptive, forward-thinking strategies has never been more pressing, as the future of cybersecurity hinges on our collective ability to combat these increasingly sophisticated threats.
Original source: thehackernews.com